
Description
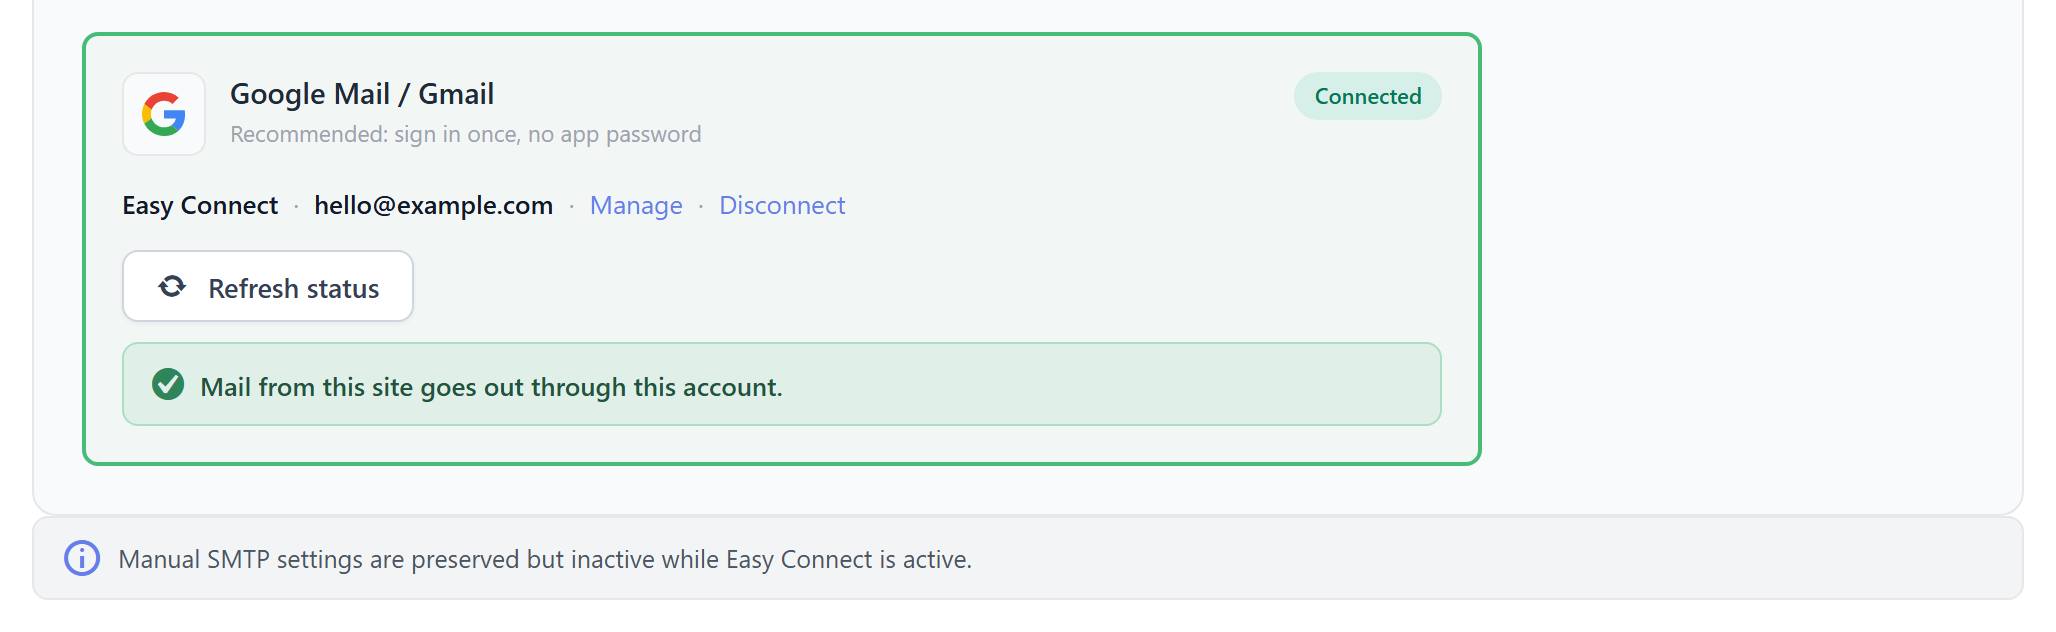
Postkeep sends your WordPress mail through Gmail without an app password: click Connect with Google, sign in, and mail starts going out through that account, even if the site sent through its own SMTP server before. The Gmail connection is a free service of allinonewpsettings.com (the makers of All-in-One WP Settings): the plugin links your site to a free account there, and that account holds the Google connection on your behalf and hands the plugin a short-lived sending token when it has mail to send. Your mail goes from your site to Google; the service never sees a message. One site per free account. The details of what is sent to the service are under “External services” below.
You do not need the service to use the plugin. Every other provider works without it: Outlook.com and Microsoft 365 (OAuth2 with your own Azure app), Yahoo, Zoho, Yandex, SendGrid, Mailgun, Amazon SES, Brevo, SparkPost, Postmark, your host’s own mail server, or any host and port you type in. Gmail also works with an app password if you prefer not to link the site.
What you get
- Gmail through the Gmail API, signed in once with no app password, with the narrow send-only permission (
gmail.send), never the full mailbox. - Any SMTP server: presets for the common providers, or your own host, port and encryption.
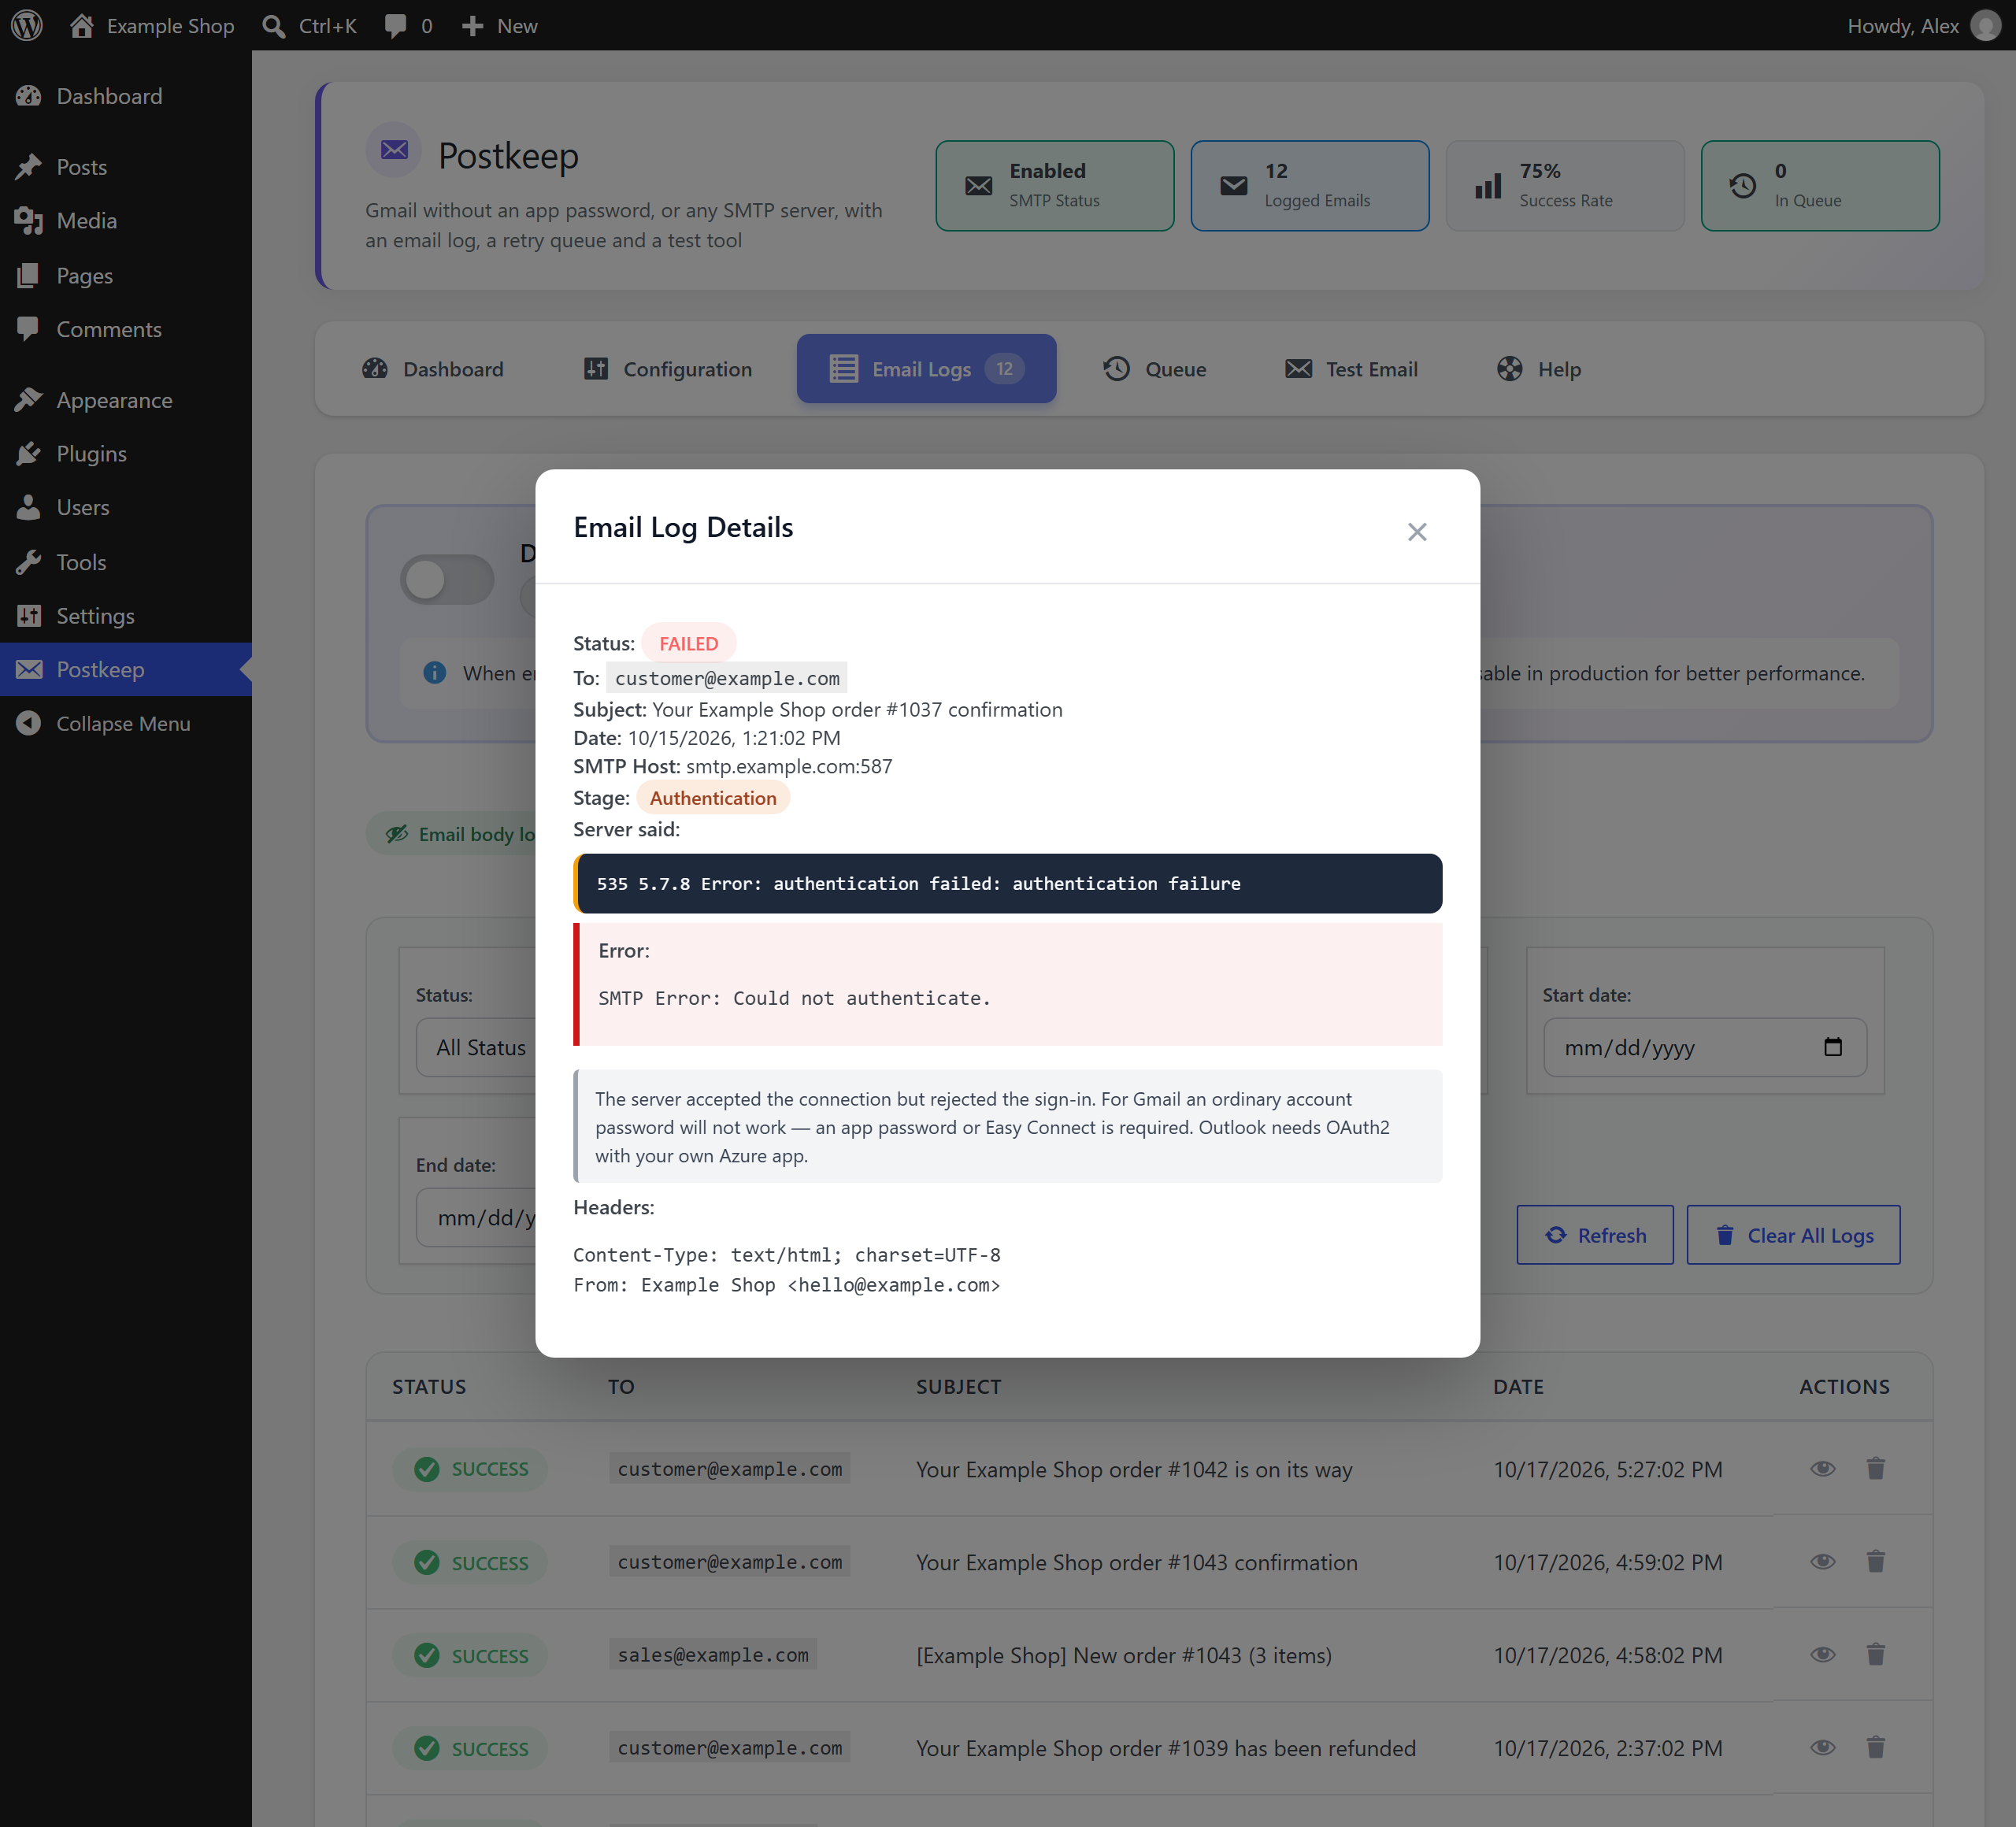
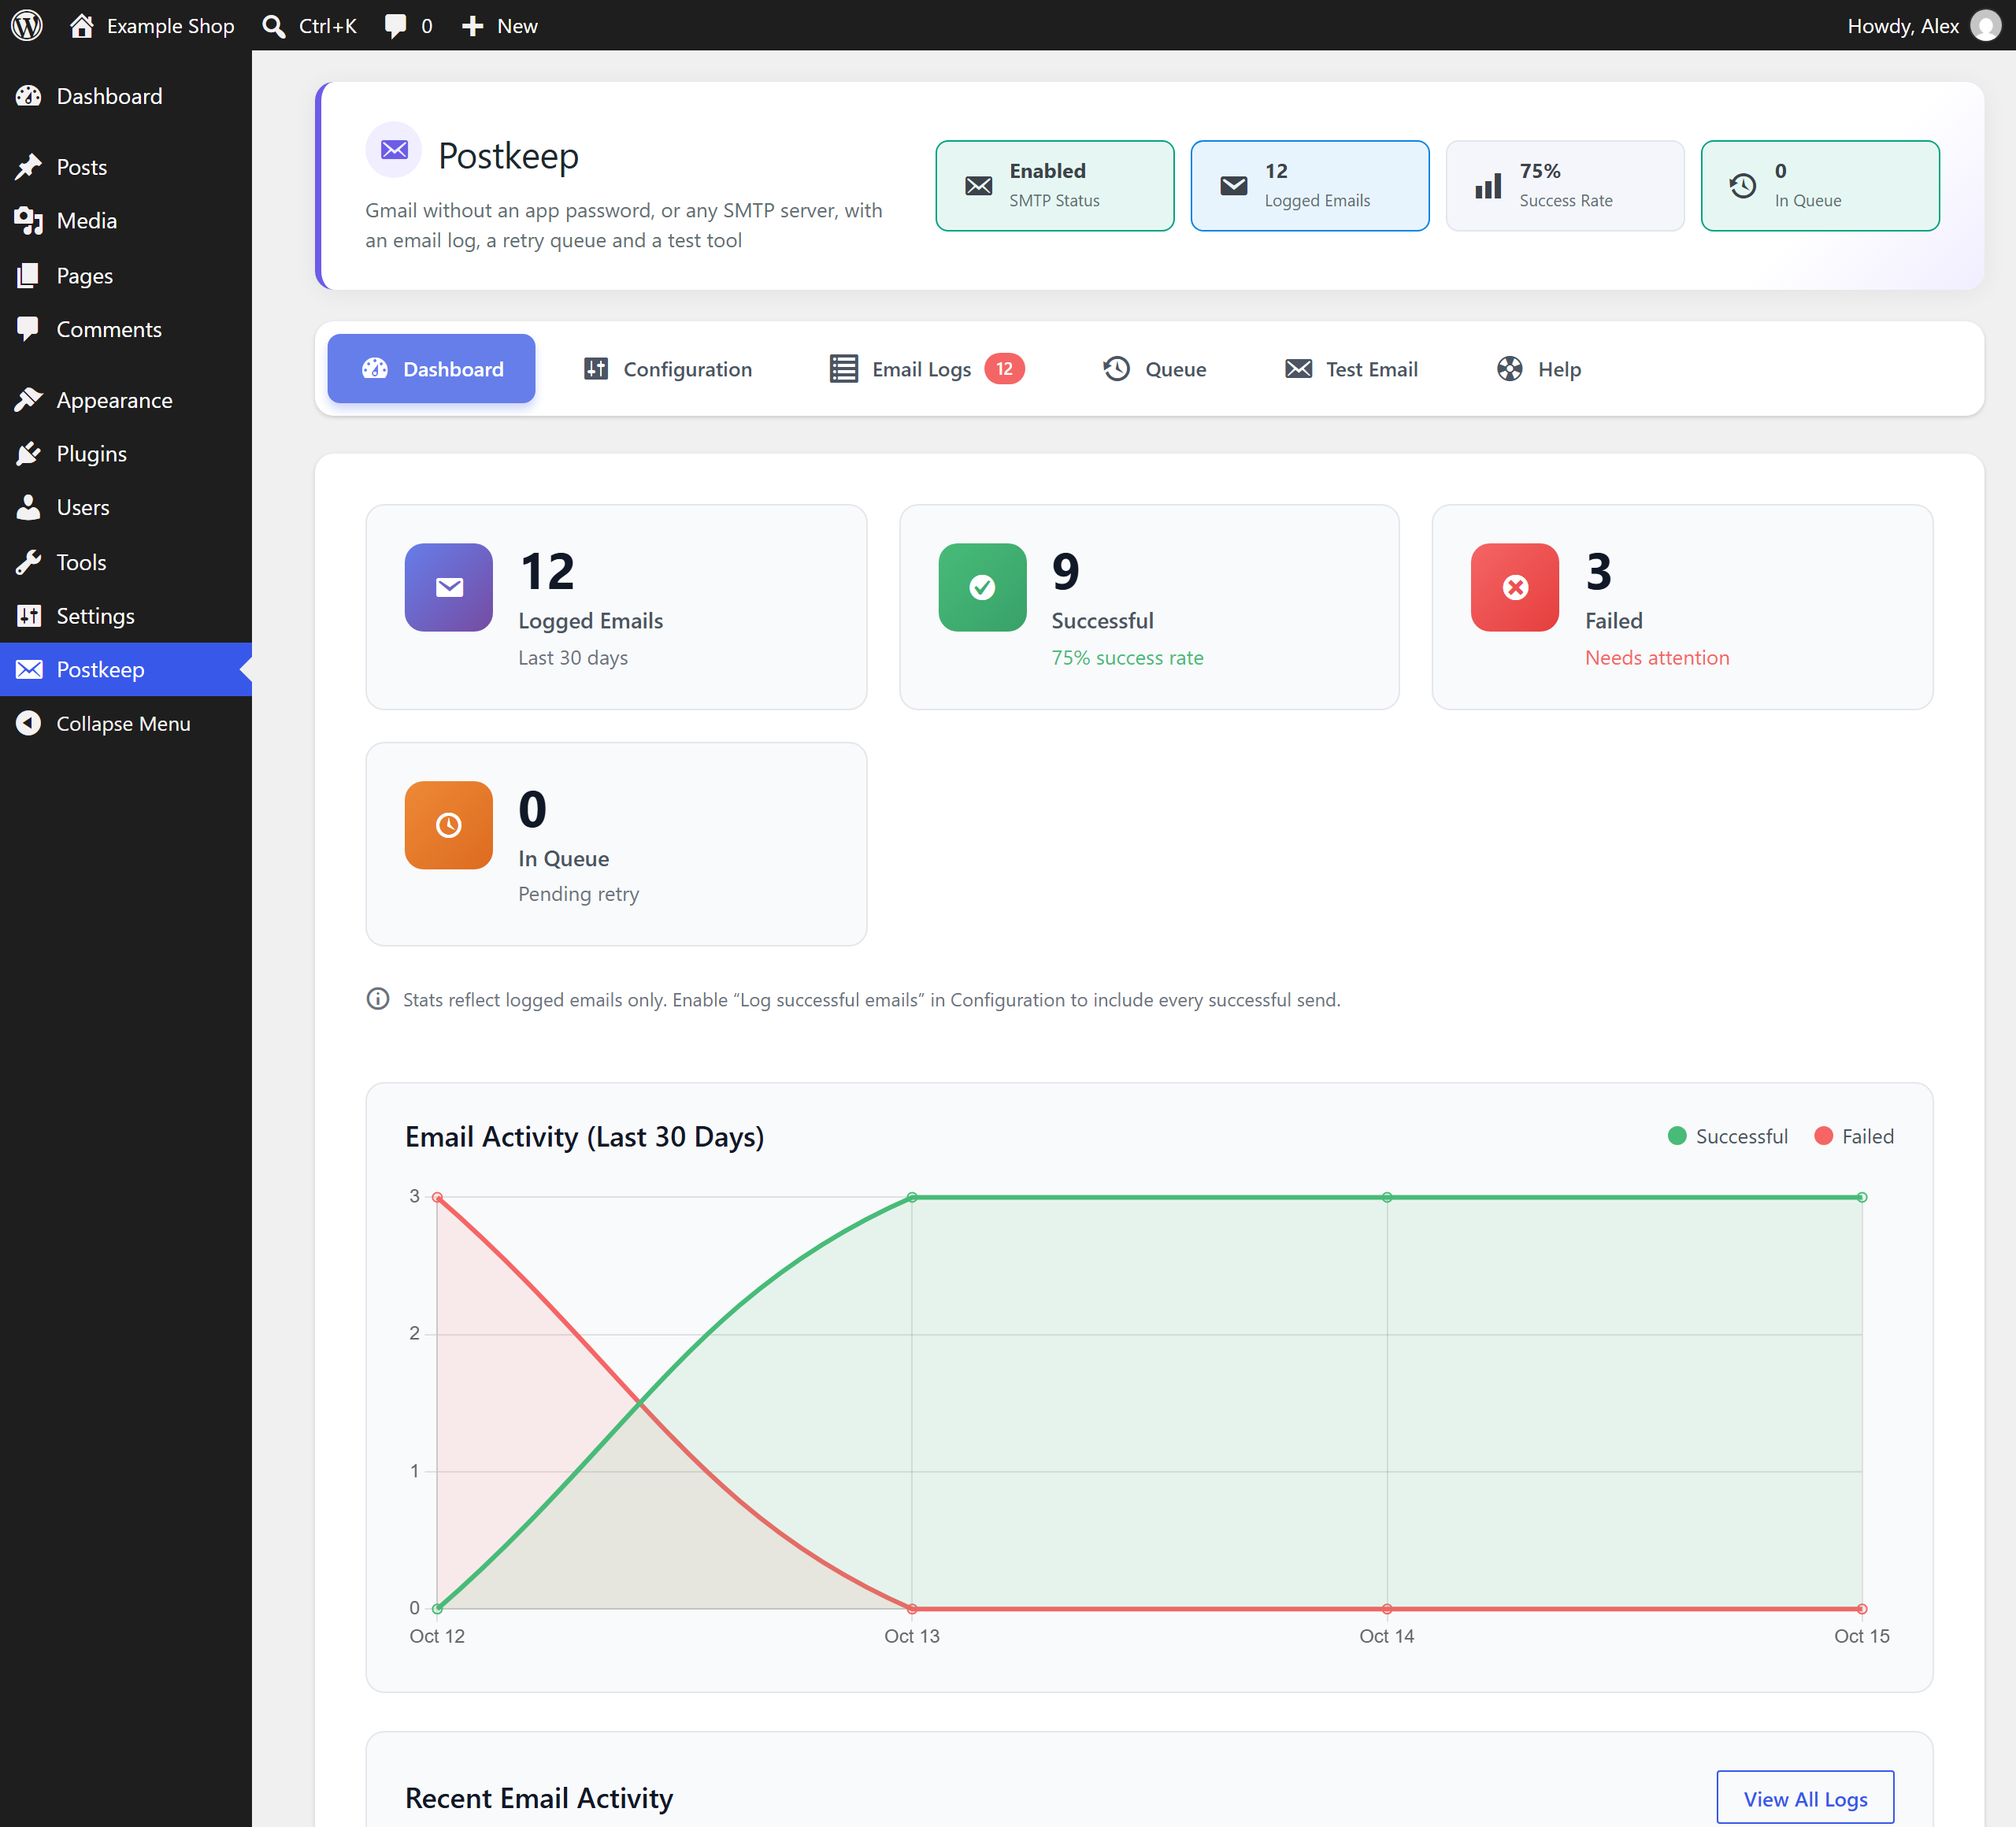
- An email log: every failed message and every test, with the reason when one failed — which stage broke (name lookup, connection, encryption, sign-in, recipient, transfer) — and the server’s own reply when it gave one, with credentials redacted. Successful messages are logged too when “Log successful emails” is on; it is off by default.
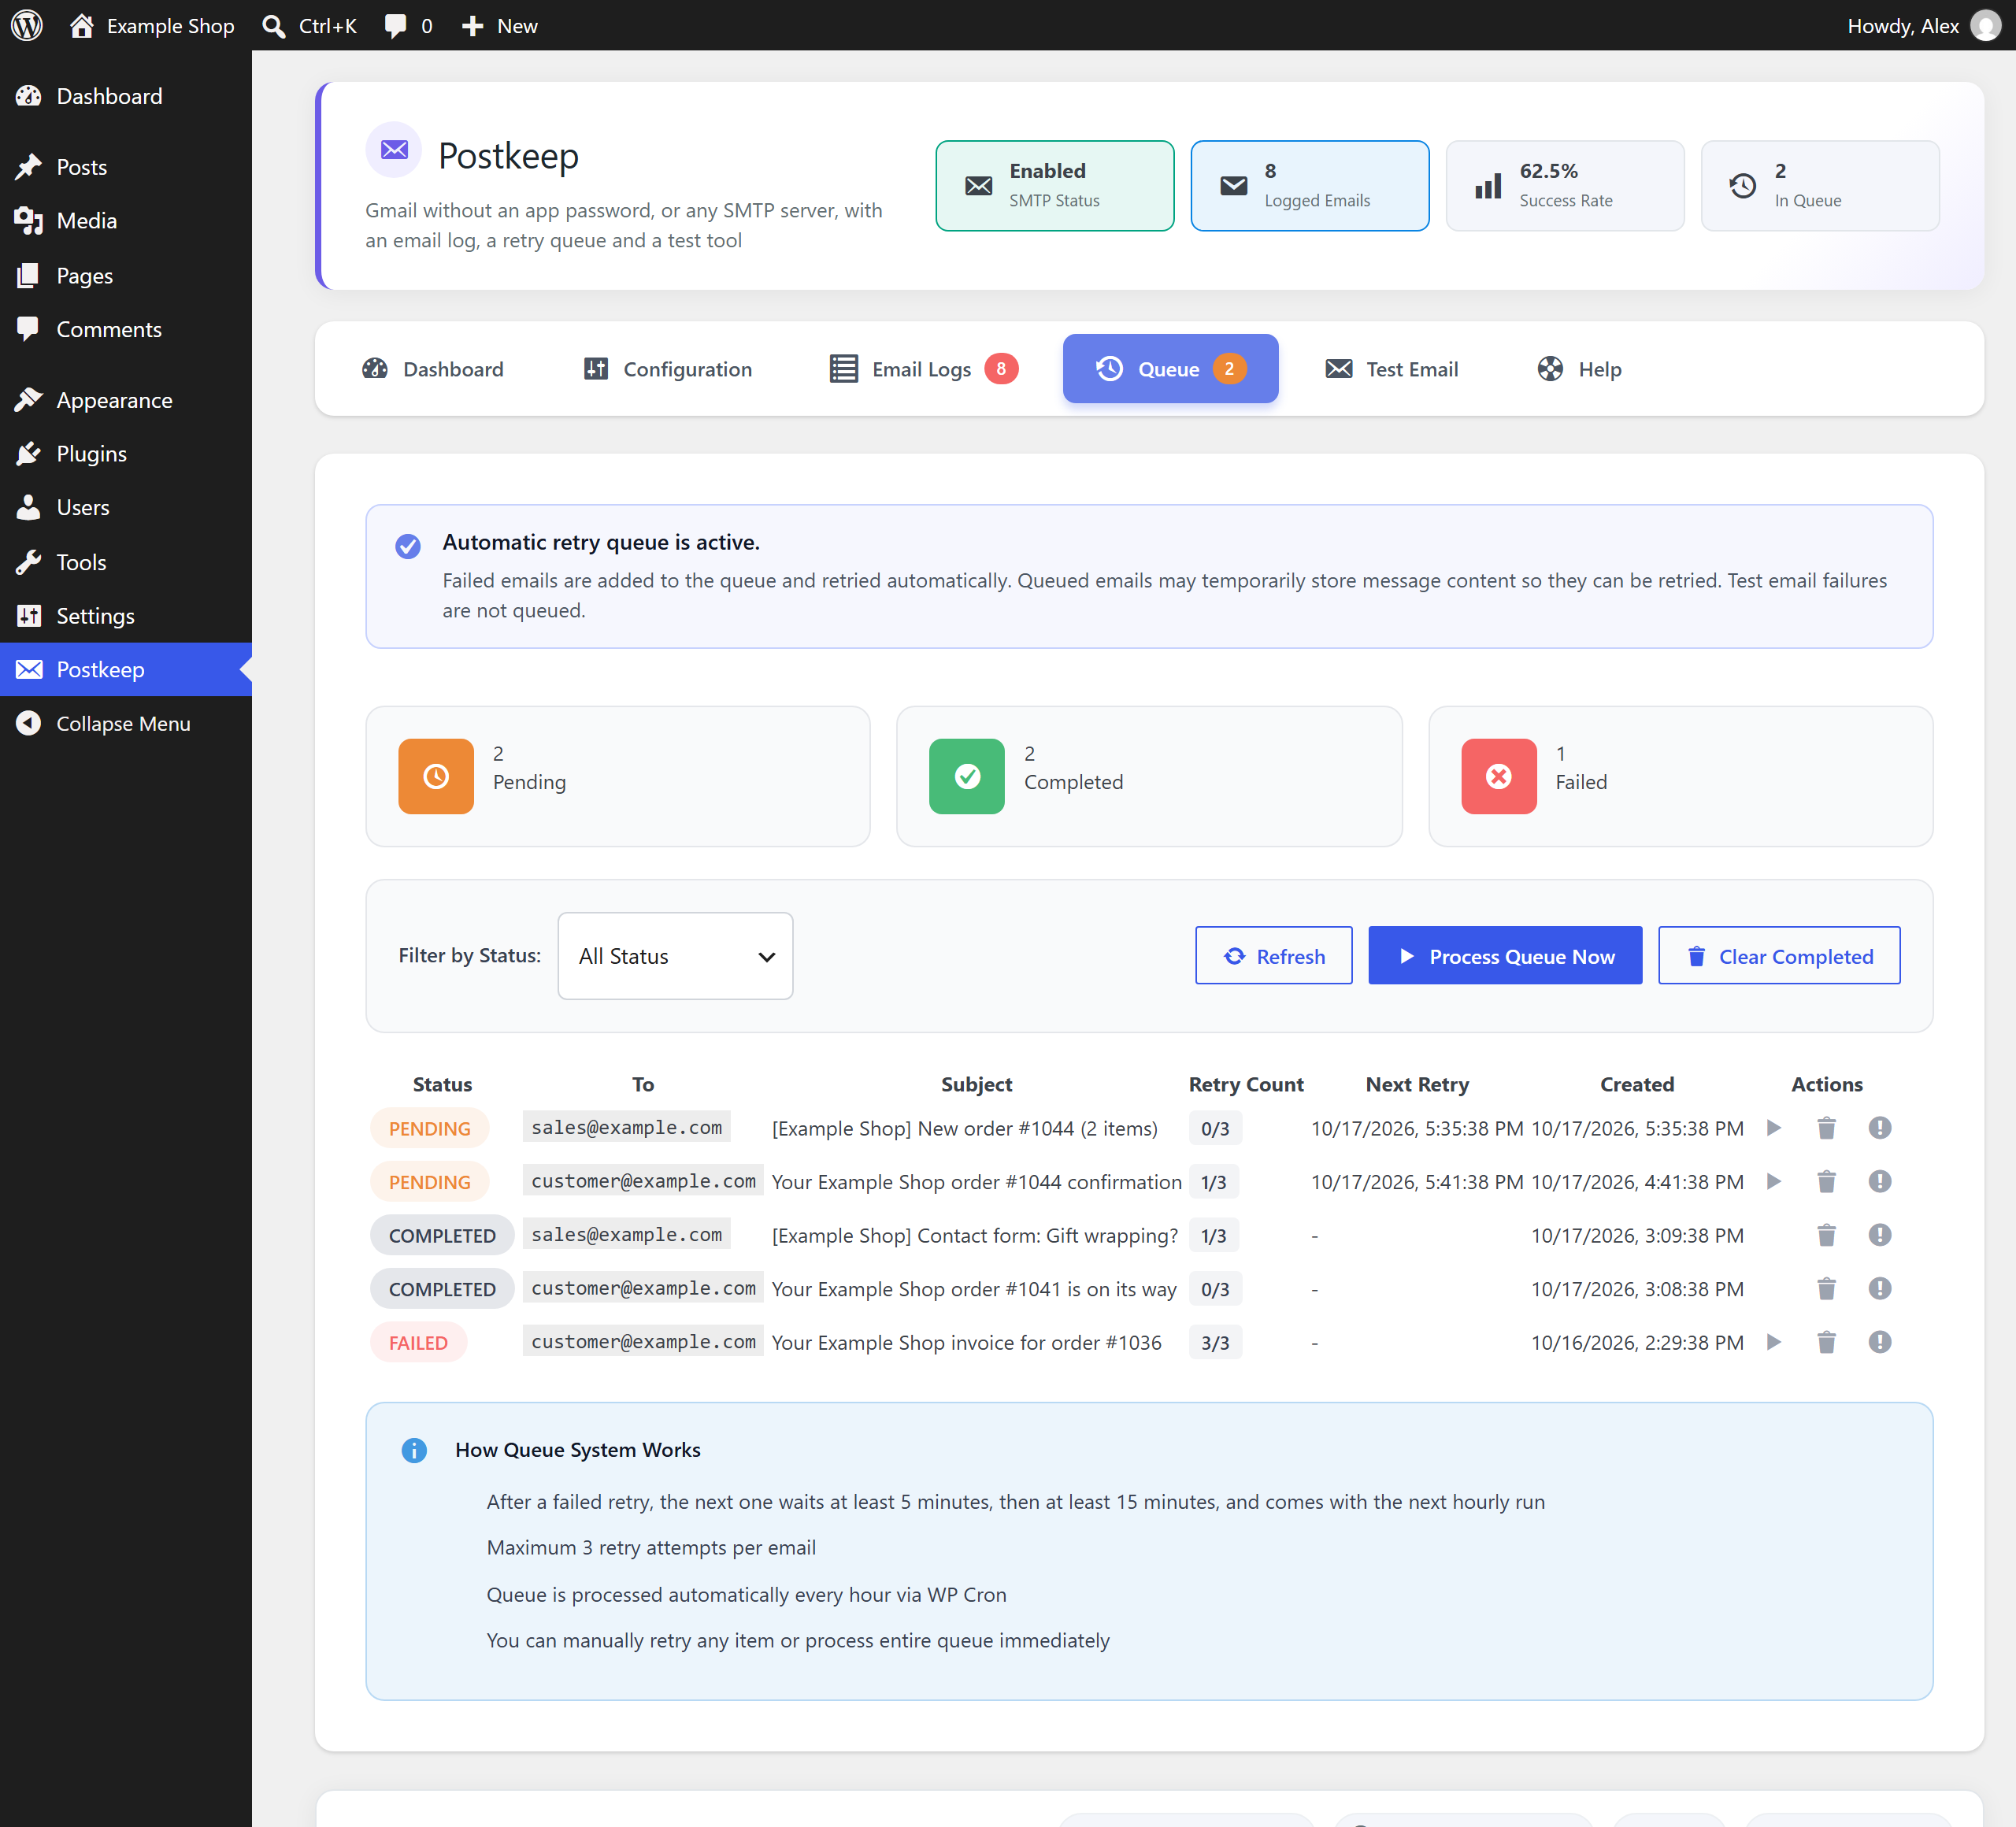
- A retry queue: when “Enable Queue System” is switched on and saved on the Configuration tab, a failed message (other than a test) is queued and tried again by an hourly scheduled task, up to three times.
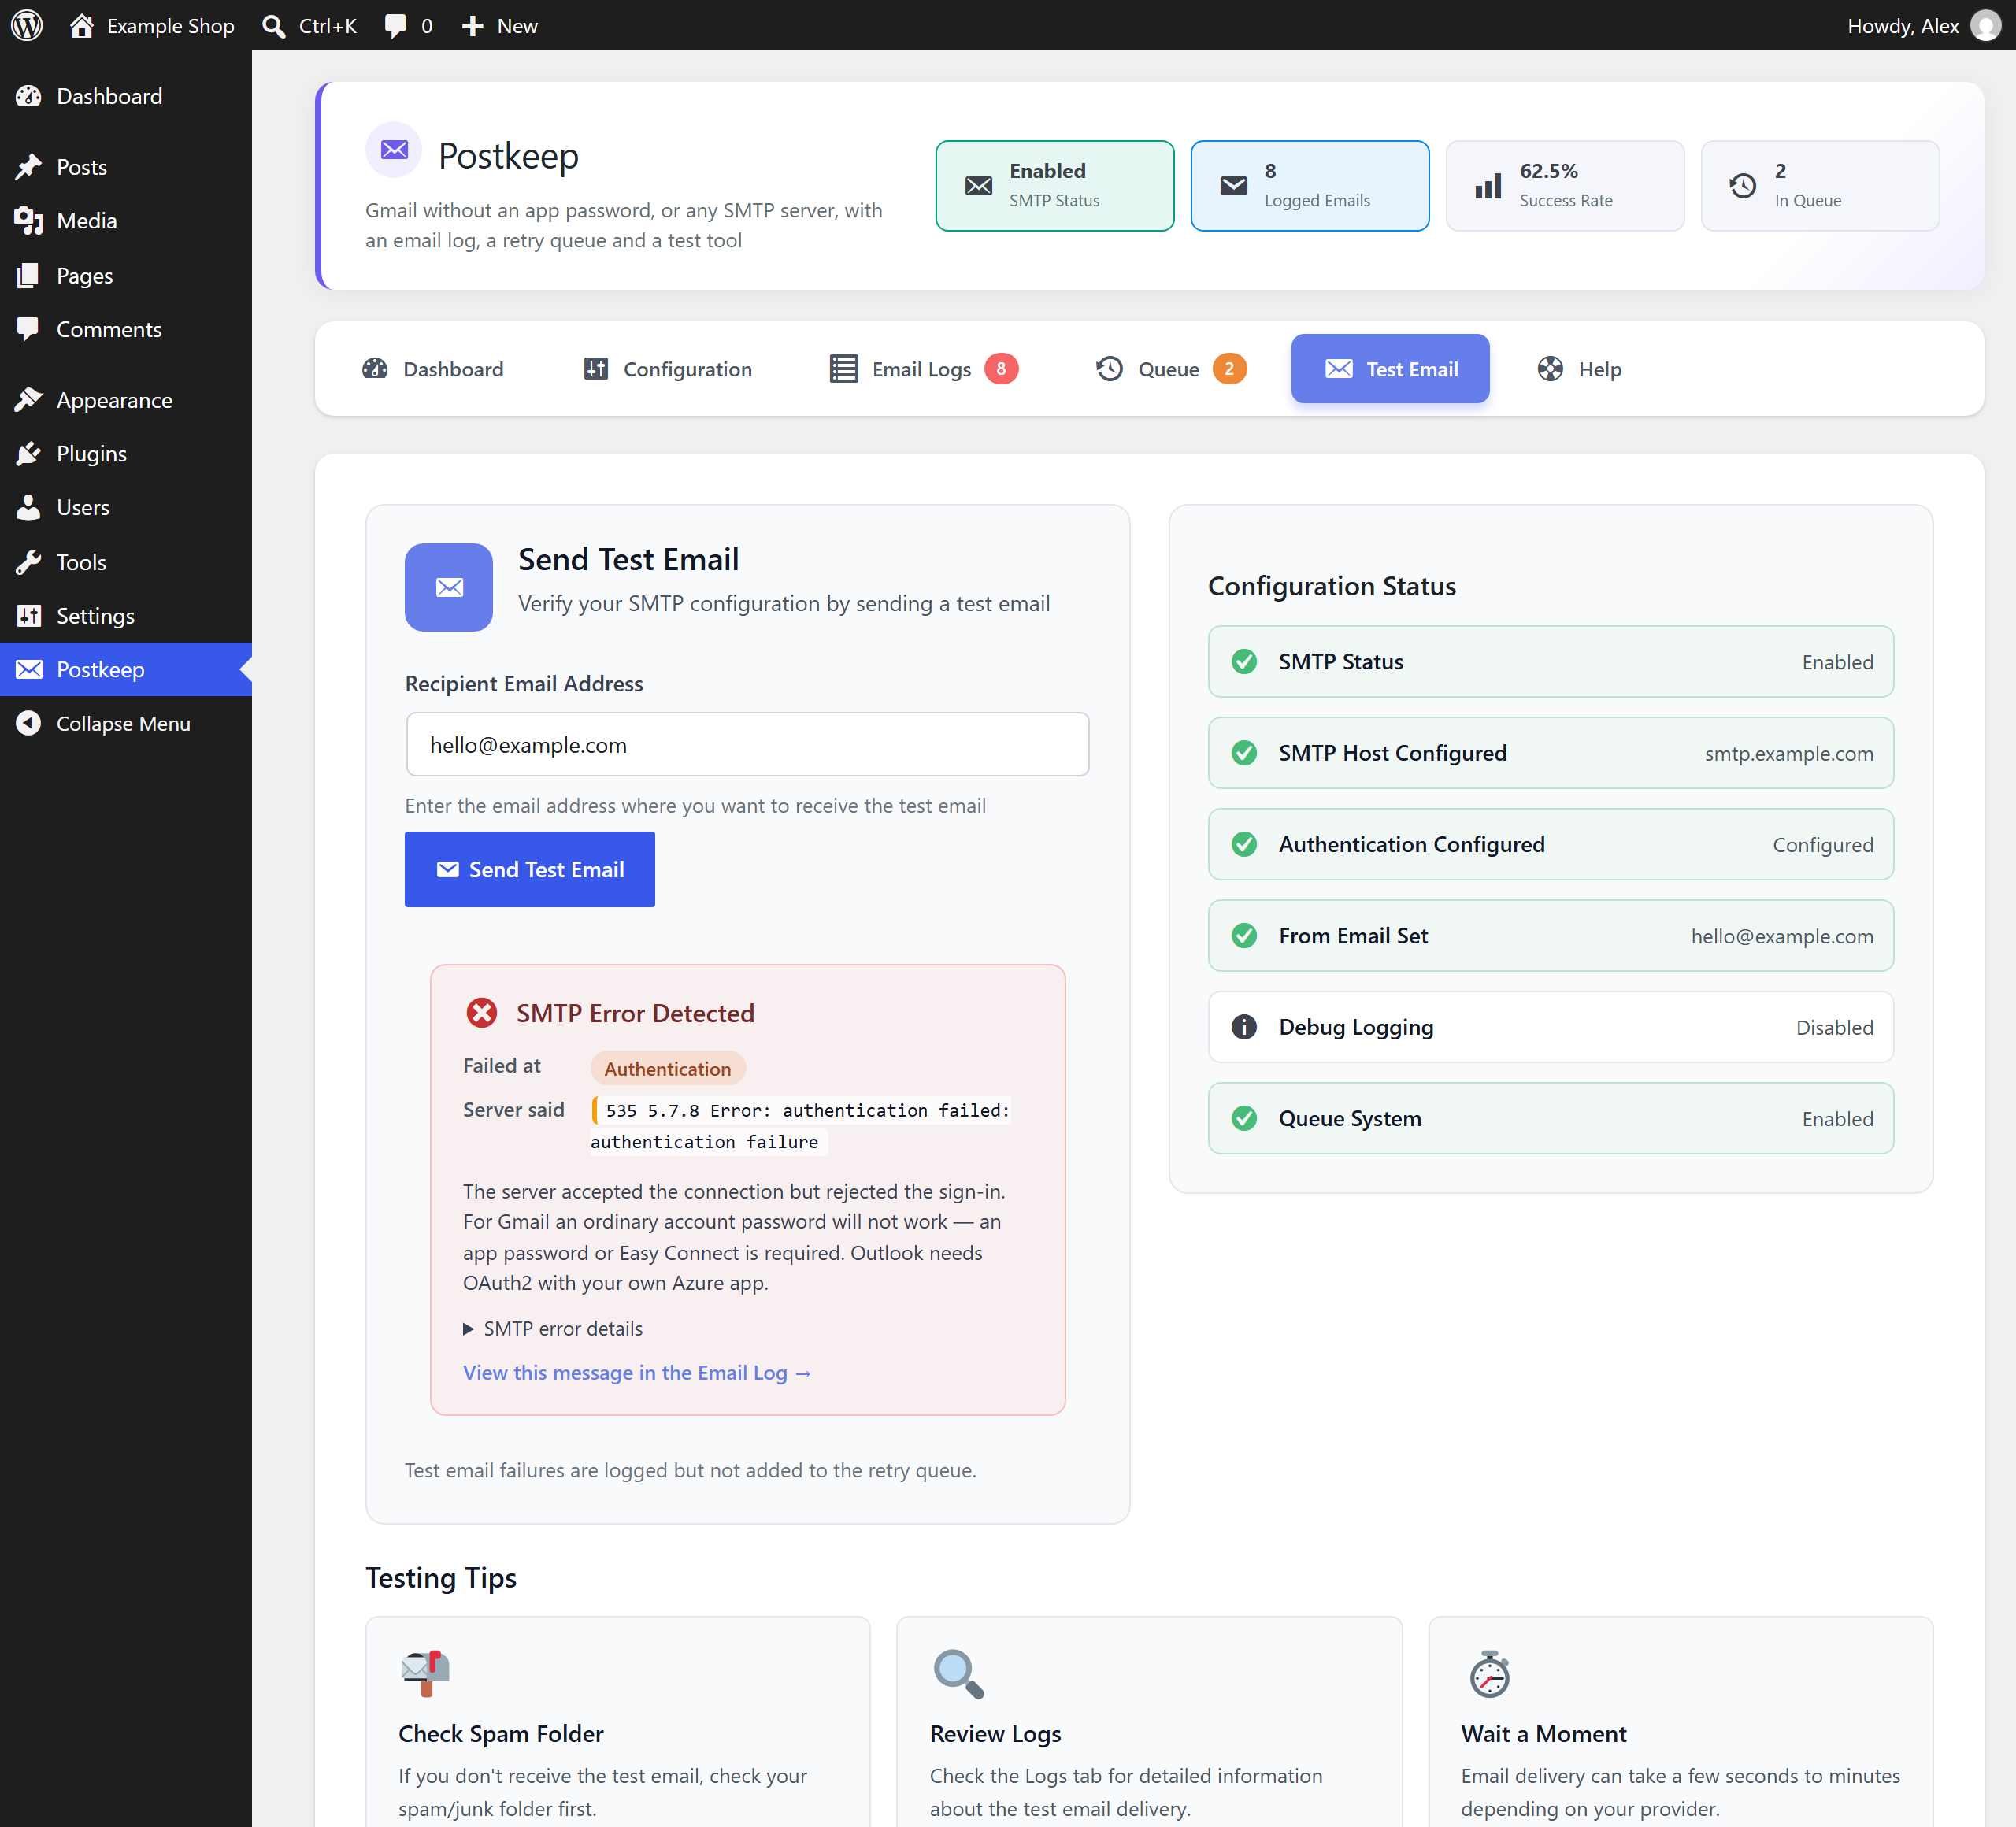
- A test tool that tells you where a failure happened instead of “could not send”.
- Passwords and tokens encrypted at rest with your site’s security keys.
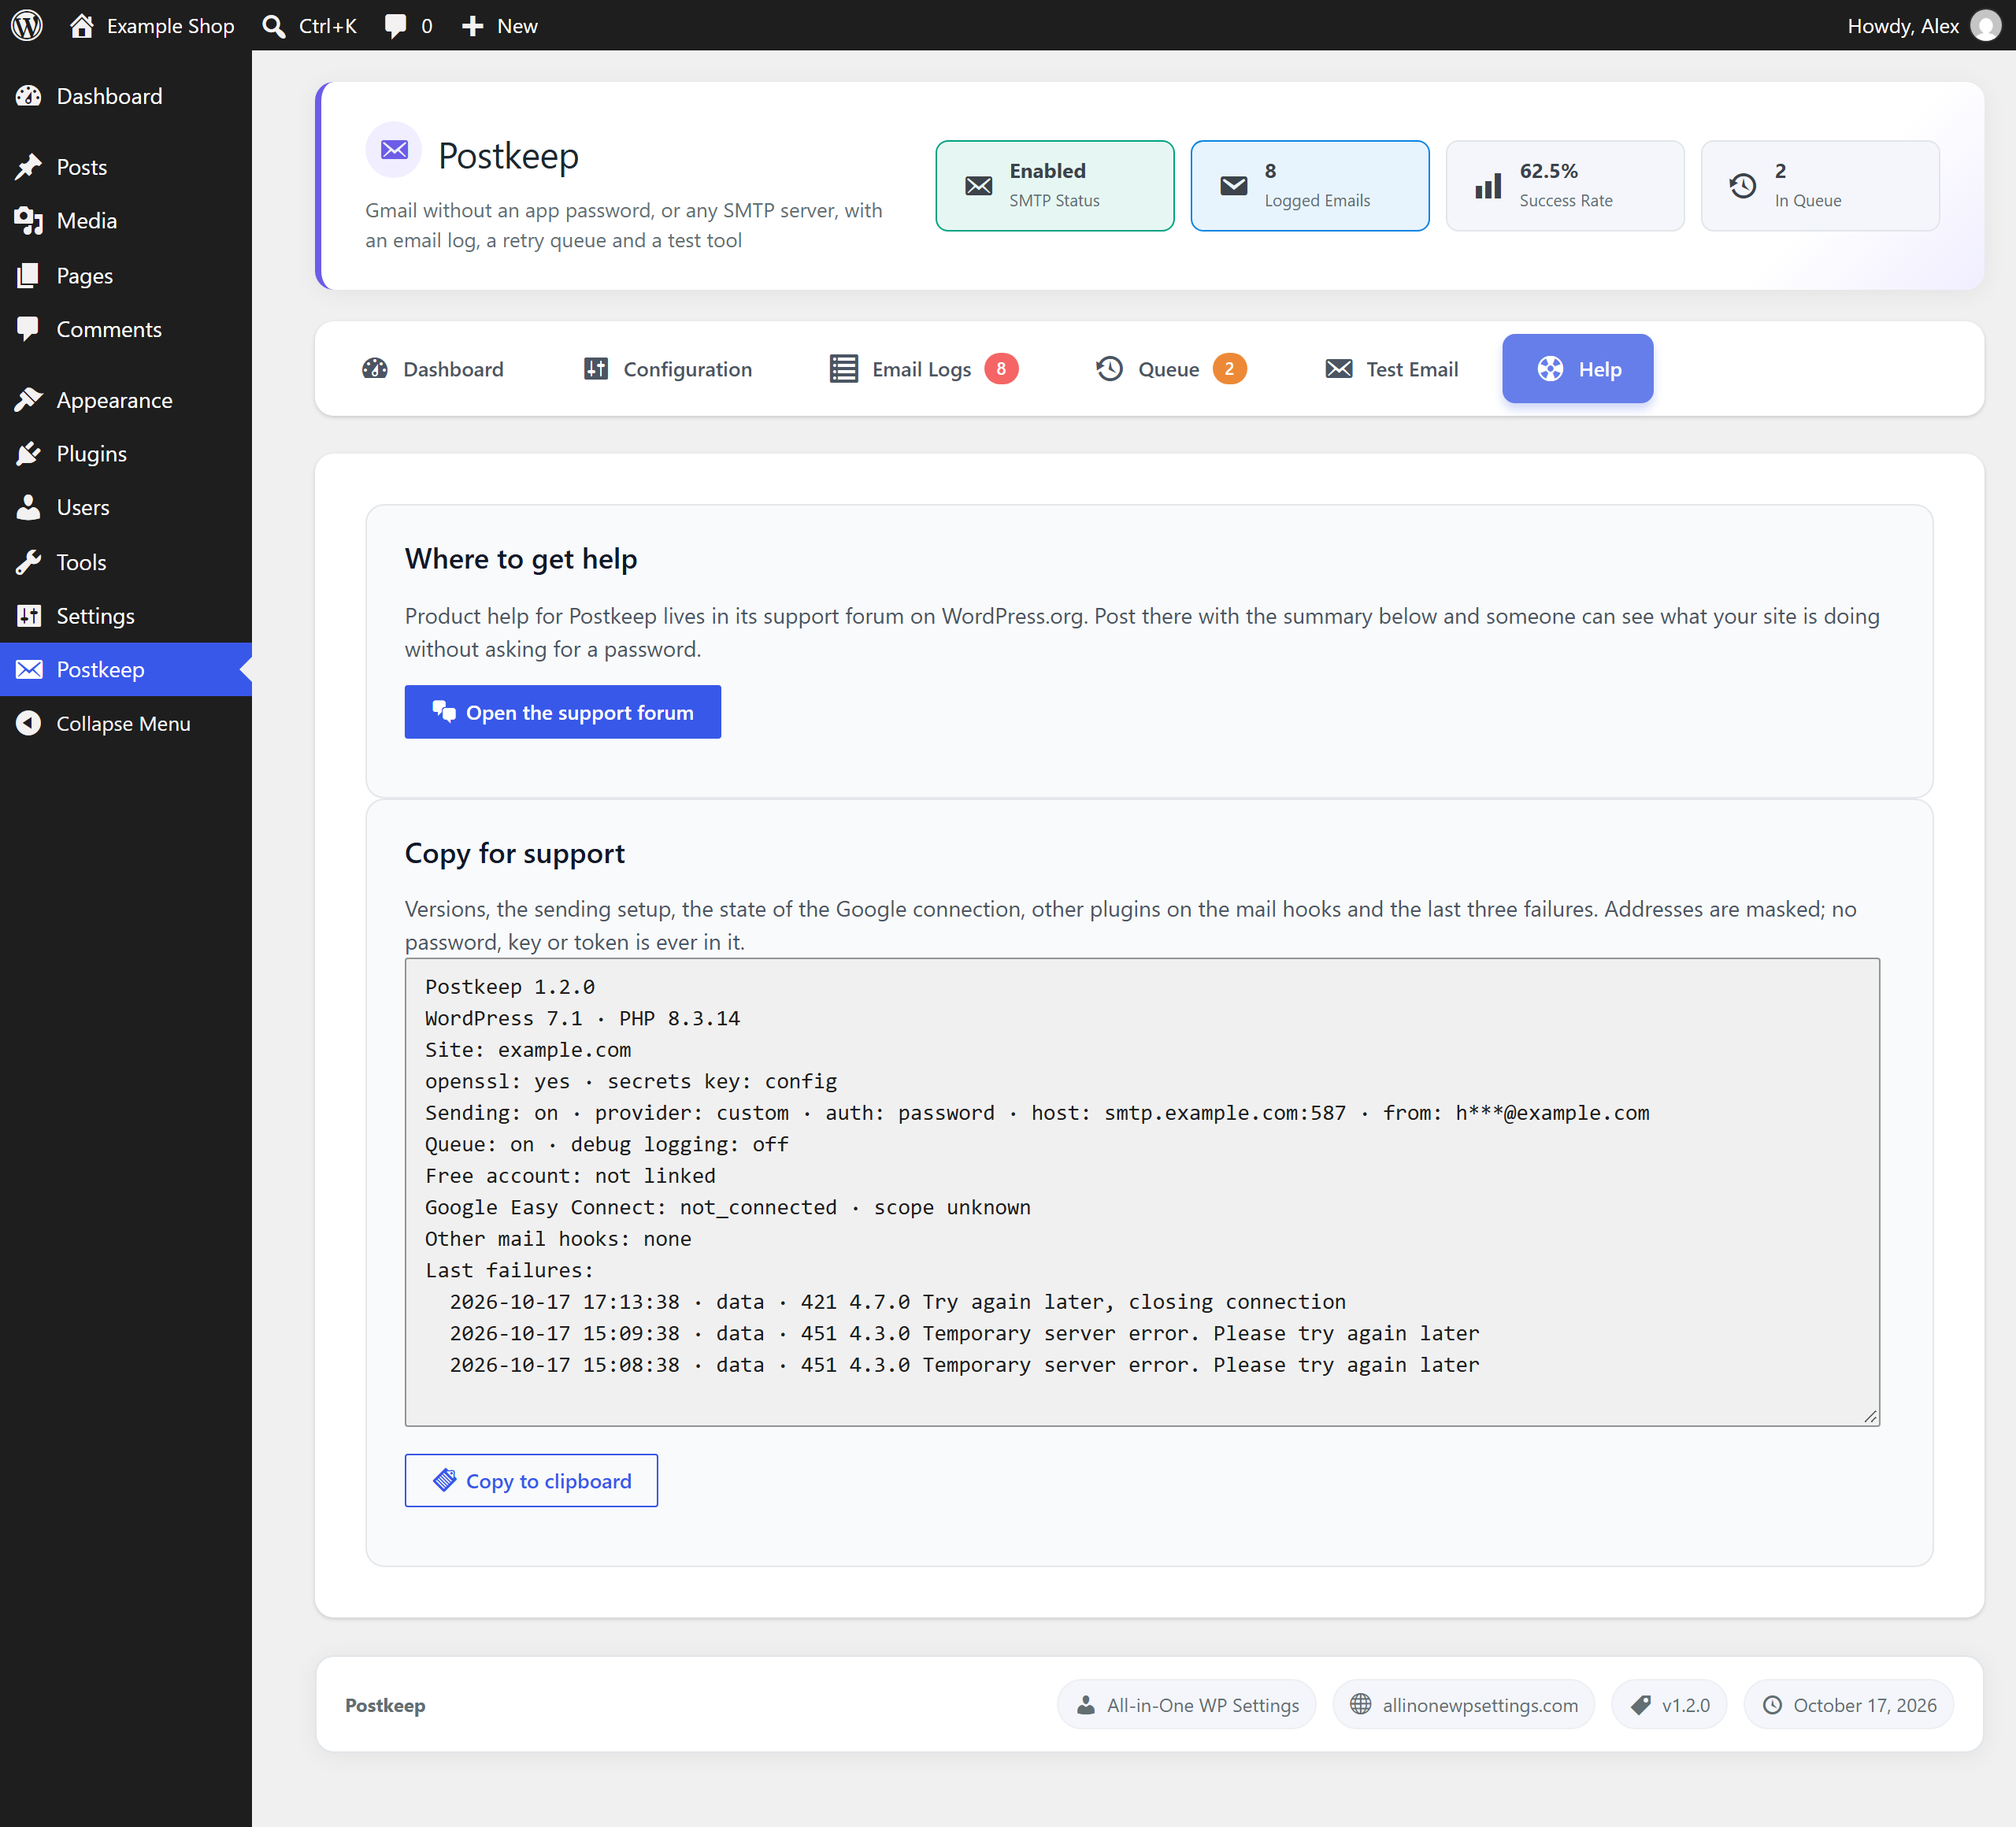
- A copy-for-support summary on the Help tab: versions, the sending setup and the last failures, ready to paste into a forum post. Passwords, tokens and the licence key are never in it, and every e-mail address in it is masked, also one a server named in a failure line.
- Every string is ready for translation on translate.wordpress.org.
Postkeep and All-in-One WP Settings
This plugin is the SMTP module of All-in-One WP Settings, offered on its own for free. If you later install the suite, it reads the same settings, log and queue, and this plugin steps aside on its own; you can then deactivate it. Nothing is lost either way.
External services
The free Gmail connection uses a service at https://allinonewpsettings.com, operated by the makers of All-in-One WP Settings. Nothing is sent to it until you click “Connect with Google”; if you never click it, the plugin contacts no external service. Once the site is linked, the calls below follow.
What is sent, and when
Every request goes to https://allinonewpsettings.com over HTTPS with a User-Agent header that names the plugin’s version and the site’s URL. Once the site is linked, every request also carries the activation token, in two request headers: Authorization: Bearer … and a second header that carries the same token. Below, “the site details” are the product code and product name, the site URL and its domain, and the plugin, WordPress and PHP versions; “the licence details” are the licence key, the activation id and the install identifier.
- Linking the site, when you click “Connect with Google” on a site that is not yet linked: the product code, the site URL, a random install identifier, the address to return to (a page of your site’s admin area), the site’s language, and the plugin, WordPress and PHP versions, to obtain a sign-in link. Your browser then opens that link and you sign in to, or register with, allinonewpsettings.com. When you are sent back, the plugin exchanges the one-time code it received, together with the site URL and the install identifier, for a licence key, an activation id and an activation token. The activation id is stored in the site’s database in plain text. The licence key and the activation token are stored encrypted with the site’s security keys; on a server without PHP’s openssl extension they are stored as they are.
- Starting the Google sign-in, straight after linking or when you click “Connect with Google” on a linked site: the site details, the licence details, the send method the plugin supports (
gmail_api), the provider and the address to return to, to obtain Google’s consent page. Google’s own consent screen then asks you for permission to send mail as you. - Reading the connection’s status: the site details without the WordPress and PHP versions, the licence details, the activation token and the supported send method, in the body of a POST request, so none of them is part of the address requested. This happens when you open the Configuration tab, unless the last answer is less than 60 seconds old; when you click “Refresh status”; and once when you come back from Google’s consent page to the Configuration or the Setup tab.
- Sending a message through the connection: the site details, the licence details, the supported send method, the provider and the purpose (
send), to obtain a short-lived Google access token. Messages sent during the same page request reuse that token. The message itself is sent from your site directly to Google’s Gmail API and never passes through the service. - Once a day, while the site is linked: the site details, the licence details and the activation token (here also in the request body), to confirm the licence is still valid.
- Disconnect, when you click it: the site details, the licence details and the supported send method, so the service revokes the Google connection.
- Deleting the plugin: the site details, the licence details and the activation token (here also in the request body), so your site leaves the free licence.
The service stores, for your free account: your e-mail address and name and your Google sign-in identifier (from signing in with Google), your language, the time of each sign-in, and a record of the terms you accepted with the date, your IP address and your browser’s user agent. For your site: its URL and domain, the install identifier, the plugin, WordPress and PHP versions and the time of the last daily check, and the IP address and browser user agent from which you linked it. For your licence: the licence key, the activation id, a one-way hash of the activation token and a history of its activations. For the Google connection: the connected Gmail address and Google account identifier, the permissions granted, a refresh token and an access token (both encrypted), when it was connected and last used, and the day’s count of sending tokens. It also keeps a record of the e-mails it sends you. The Google tokens are deleted when you click Disconnect, 30 days after the plugin is deleted, or after 180 days without sending; the Gmail address and Google account identifier are deleted 90 days after the tokens. The rest is kept with no set end date. The service never receives a message, a recipient or your Gmail password.
Terms of service: https://allinonewpsettings.com/terms-of-service
Privacy policy: https://allinonewpsettings.com/privacy-policy
The mail providers themselves
Sending mail means talking to the provider you chose, with your own account. Those requests go from your site straight to the provider; nothing here passes through allinonewpsettings.com. They happen only for the provider you have configured, and only when your site sends mail or when you connect an account.
- Google — sending. When Gmail is your provider and the account is connected (through the free Gmail connection above, or through your own Google app), each message is posted to the Gmail API at https://gmail.googleapis.com —
/gmail/v1/users/me/messages/send, or/upload/gmail/v1/users/me/messages/sendwhen the message with its attachments, encoded for the API, is larger than 4 MiB (about 3 MiB before encoding). What is sent is the message itself: your sender name and address, the recipients, the subject, the body and any attachments, with the access token for your account. Google’s terms: https://policies.google.com/terms — Google’s privacy policy: https://policies.google.com/privacy - Google — signing in with your own app. If you enter your own Google Client ID and Secret instead of using the free Gmail connection, your browser is sent to https://accounts.google.com to approve it, and the plugin then exchanges the result for tokens at https://oauth2.googleapis.com/token, and refreshes them there. What is sent: your Client ID, your Client Secret and the code or refresh token. Same terms and privacy policy as above.
- Microsoft — sending and signing in. With Outlook.com or Microsoft 365 and your own Azure app, your browser is sent to https://login.microsoftonline.com to approve it; the plugin exchanges and refreshes tokens at the same host, reads the mailbox address once from https://graph.microsoft.com/v1.0/me, and posts each message to https://graph.microsoft.com/v1.0/me/sendMail — what is sent: your Client ID and Secret at sign-in, and afterwards the message — sender, recipients, subject, body and attachments. Microsoft Services Agreement: https://www.microsoft.com/en-us/servicesagreement — Microsoft privacy statement: https://www.microsoft.com/en-us/privacy/privacystatement
- Yahoo — signing in. With Yahoo Mail and OAuth2, your browser is sent to https://api.login.yahoo.com to approve your own app, and tokens are exchanged and refreshed at the same host; the mail itself then goes over SMTP to Yahoo’s mail server. What is sent: your Client ID, your Client Secret and the code or refresh token. Yahoo’s terms: https://legal.yahoo.com/us/en/yahoo/terms/otos/index.html — Yahoo’s privacy policy: https://legal.yahoo.com/us/en/yahoo/privacy/index.html
Every other provider — SendGrid, Mailgun, Amazon SES, Brevo, SparkPost, Postmark, Zoho, Yandex, your host’s own mail server, or any host you type in — is reached over plain SMTP at the address you enter, with the credentials you enter, and nowhere else.
The provider list on the settings screen
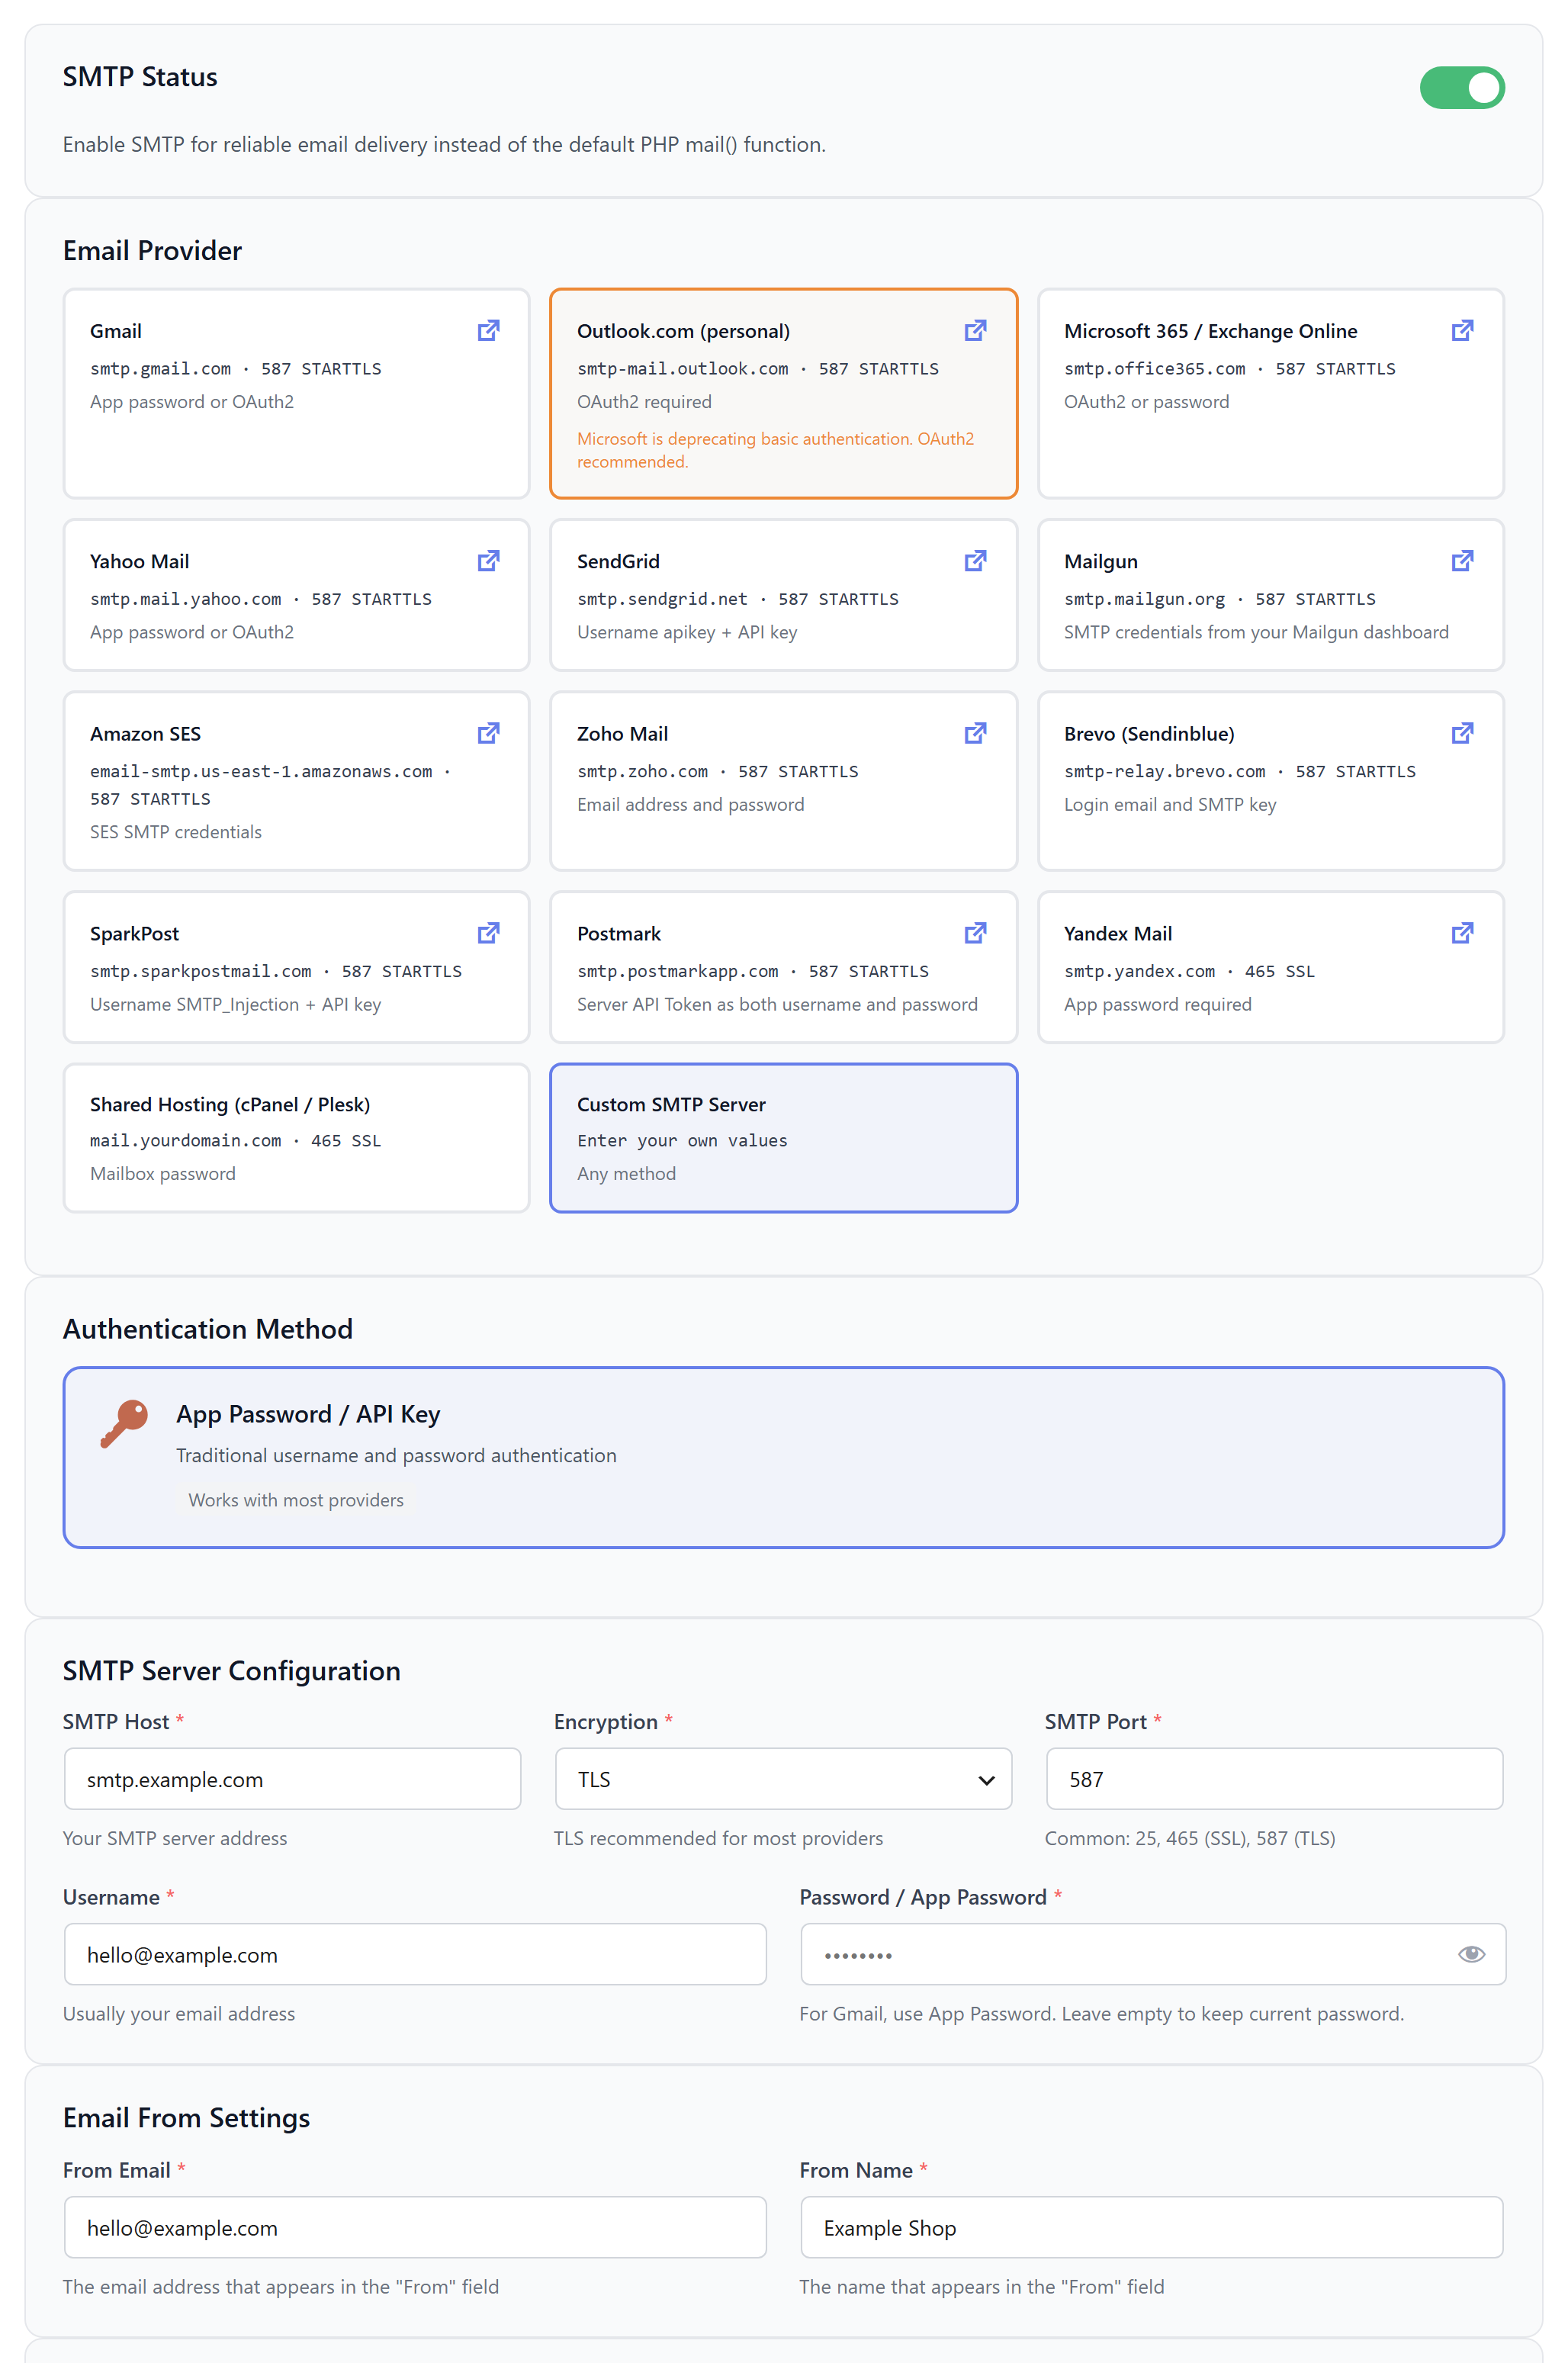
The settings screen offers thirteen providers to pick from, and each one is a saved set of starting values for the form: a port and an encryption setting, and, for the eleven named services, their mail server — such as email-smtp.us-east-1.amazonaws.com for Amazon SES or smtp.sendgrid.net for SendGrid — and a link to that provider’s own setup documentation, for example https://developers.sparkpost.com/api/smtp/ for SparkPost. (“Shared Hosting” fills in mail. and your own domain, with port 465 and SSL; “Custom SMTP Server” leaves the server empty and starts with port 587 and TLS. Neither has a documentation link.) Picking a provider fills the form in for you; nothing is contacted when you pick one, and the documentation link only opens in your browser if you click it. The plugin sends mail to the server in the form after you have saved it, with the credentials you entered, and it contacts no other address. So the provider names and hostnames in the plugin’s code are a list of choices available to you, not services this plugin talks to: a site that never picks Amazon SES never reaches Amazon, and the same for every other name on the list.
One more address appears in the plugin’s code and is not a service it contacts: https://api.wordpress.org/secret-key/1.1/salt/ is named in an admin message that tells you where to generate WordPress’s security keys when your wp-config.php has none. It is text in a warning on your own screen; the plugin makes no request to it.
Screenshots
Installation
- Install it from Plugins > Add Plugin (search for Postkeep), or upload it to
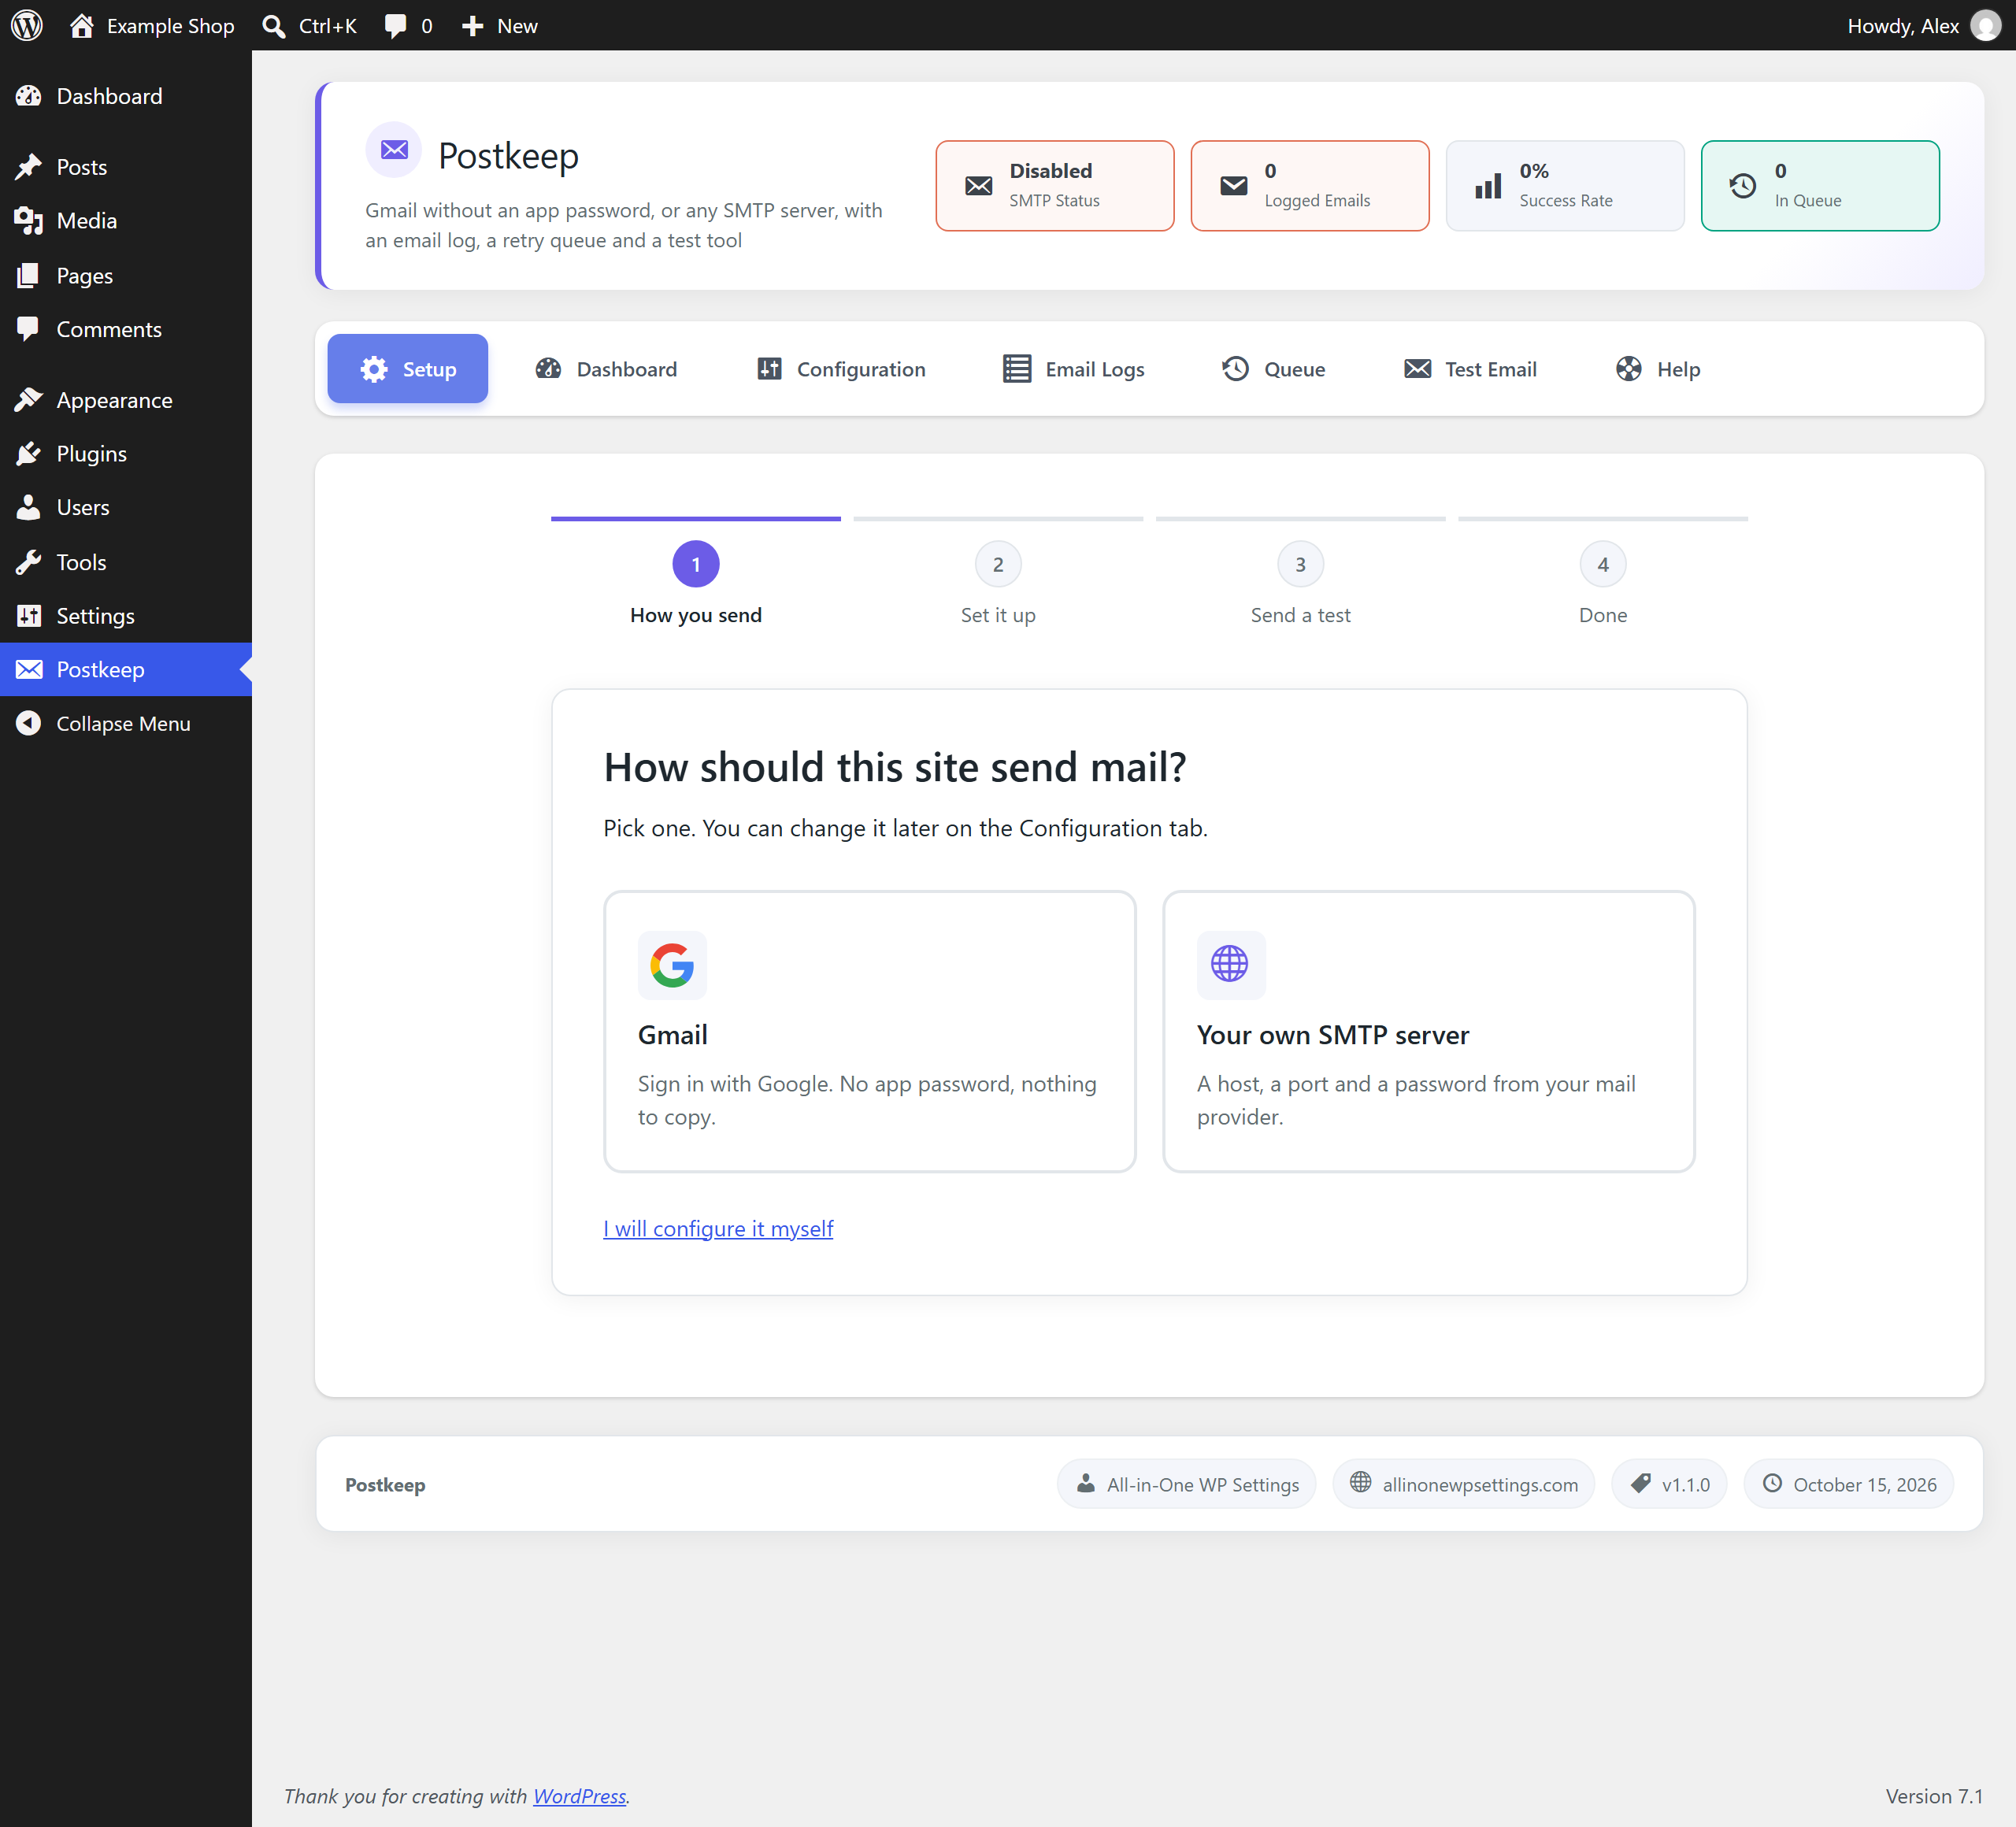
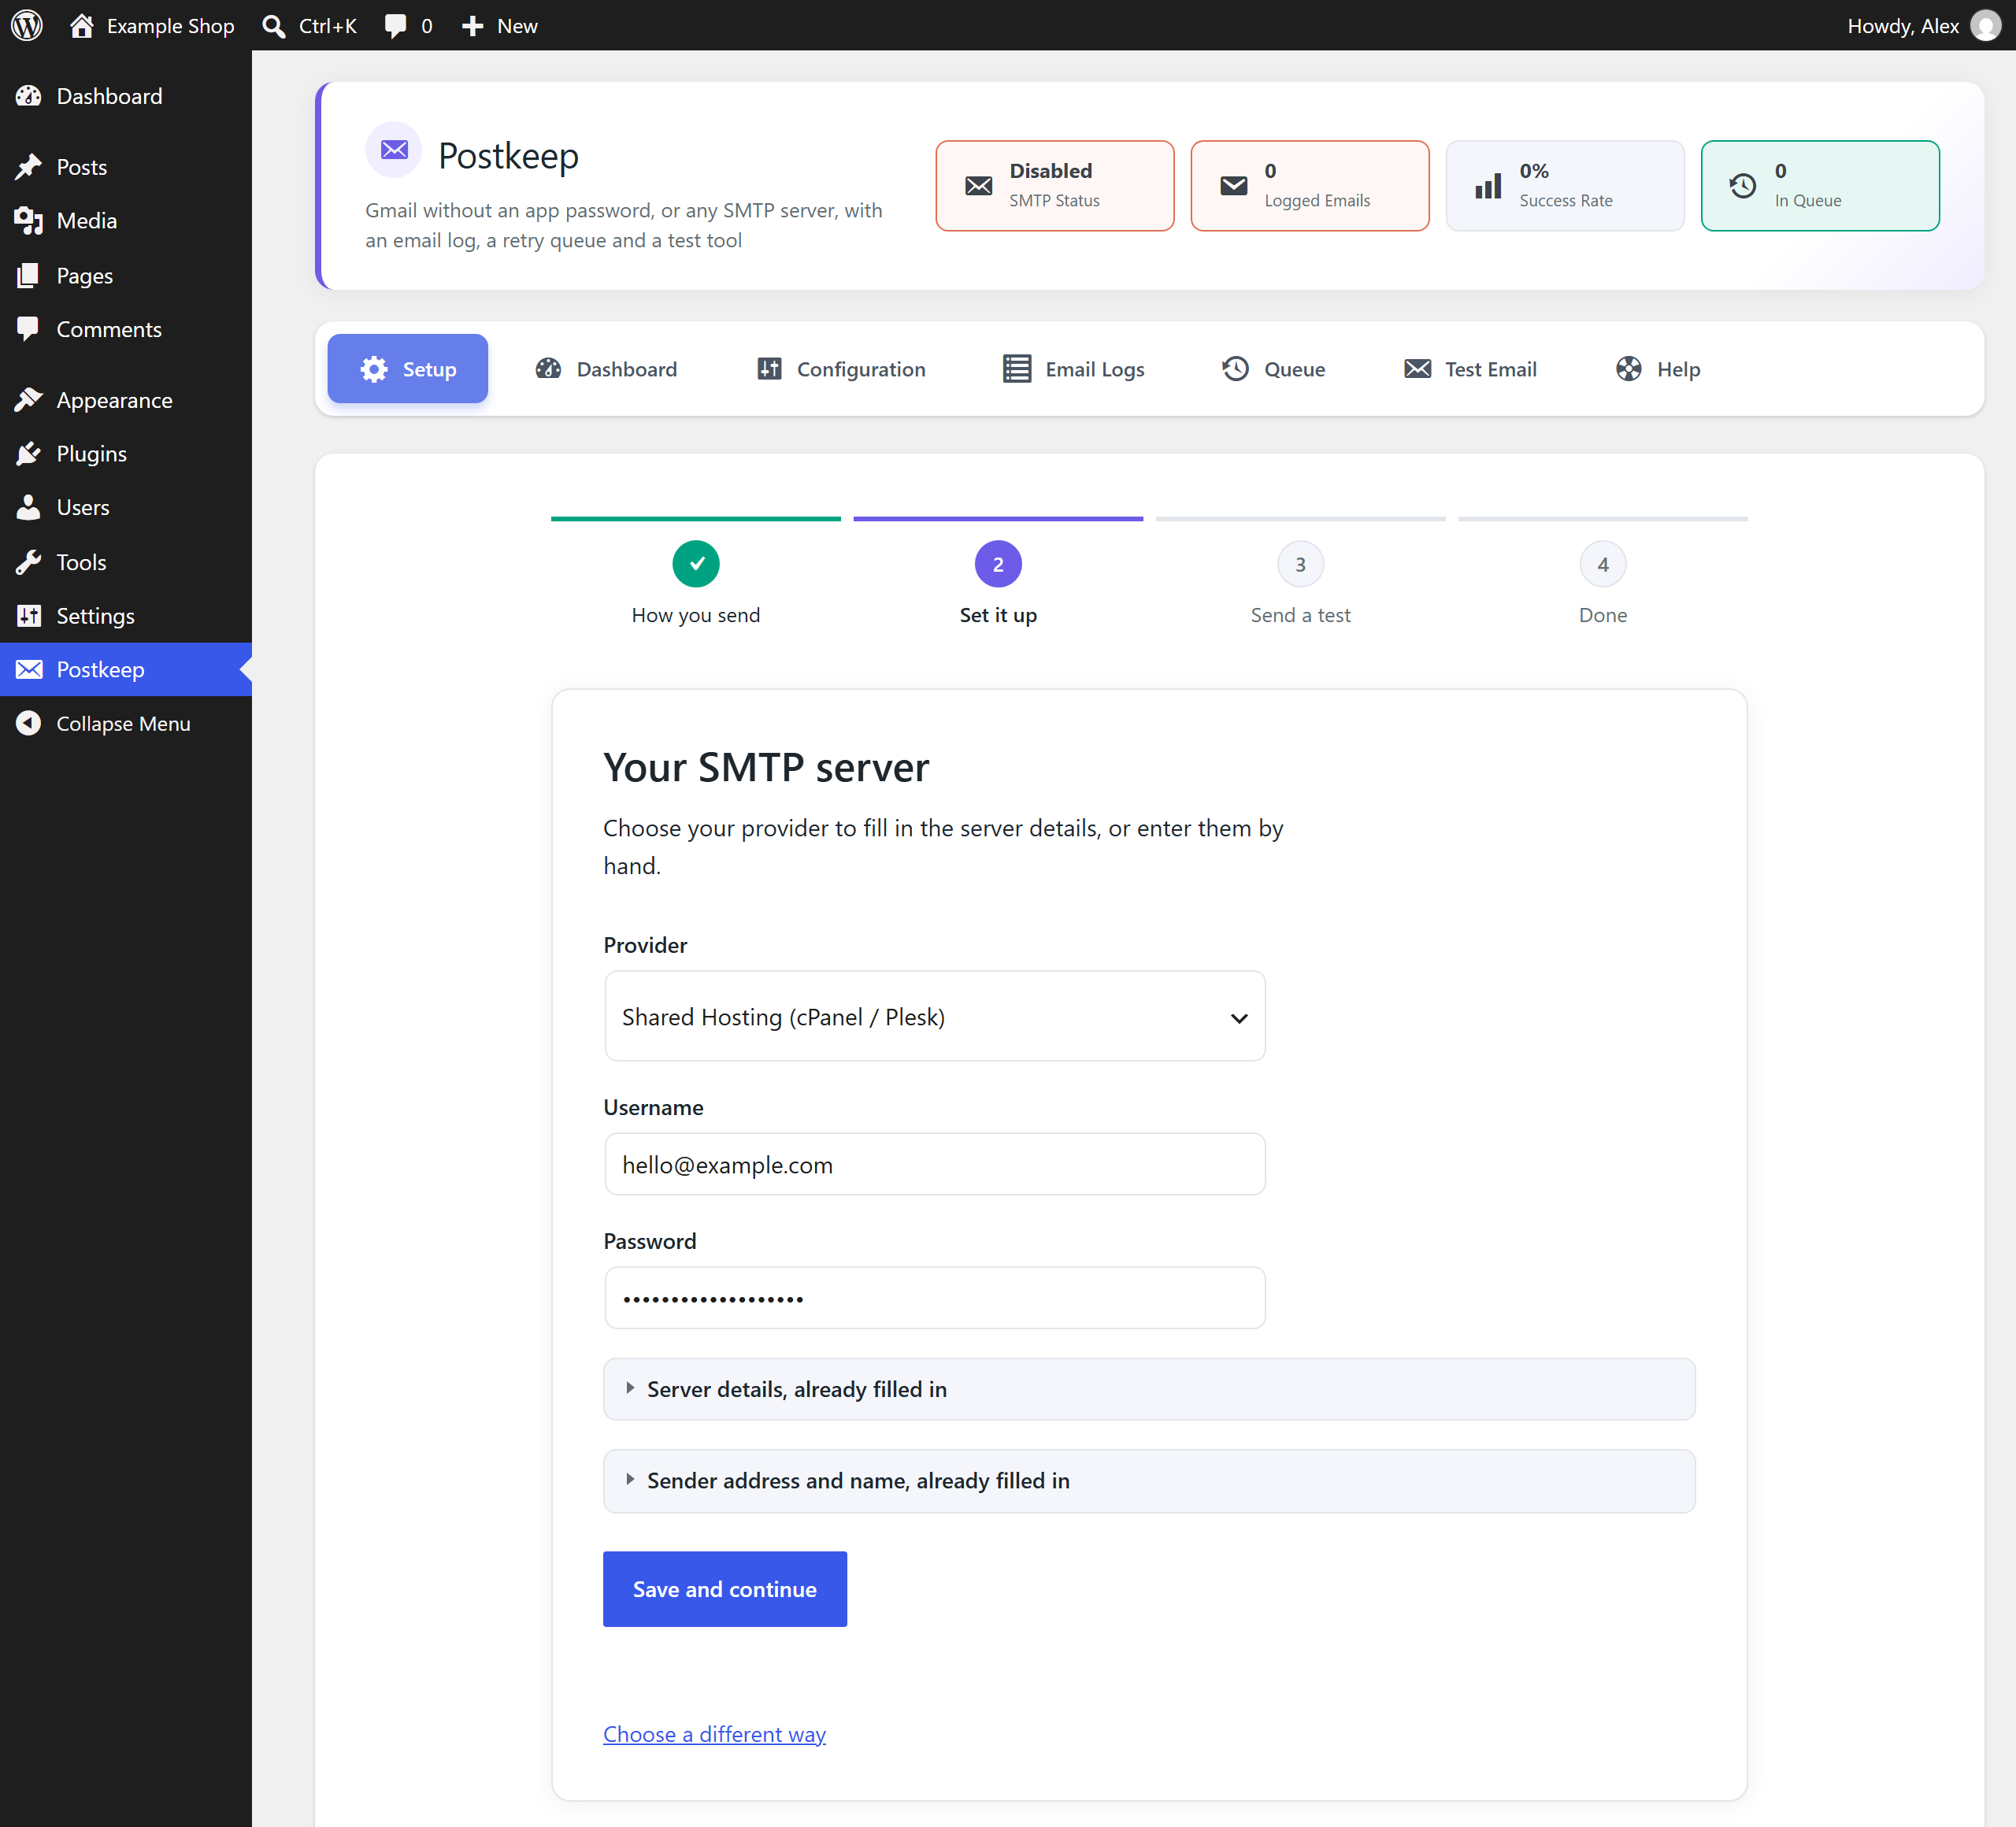
/wp-content/plugins/postkeep/. - Activate it. The setup wizard opens: choose Gmail or your own SMTP server, enter the details, and send a test email.
- Prefer to do it by hand? Choose “I will configure it myself” in the wizard, or open the Configuration tab under Postkeep at any time.
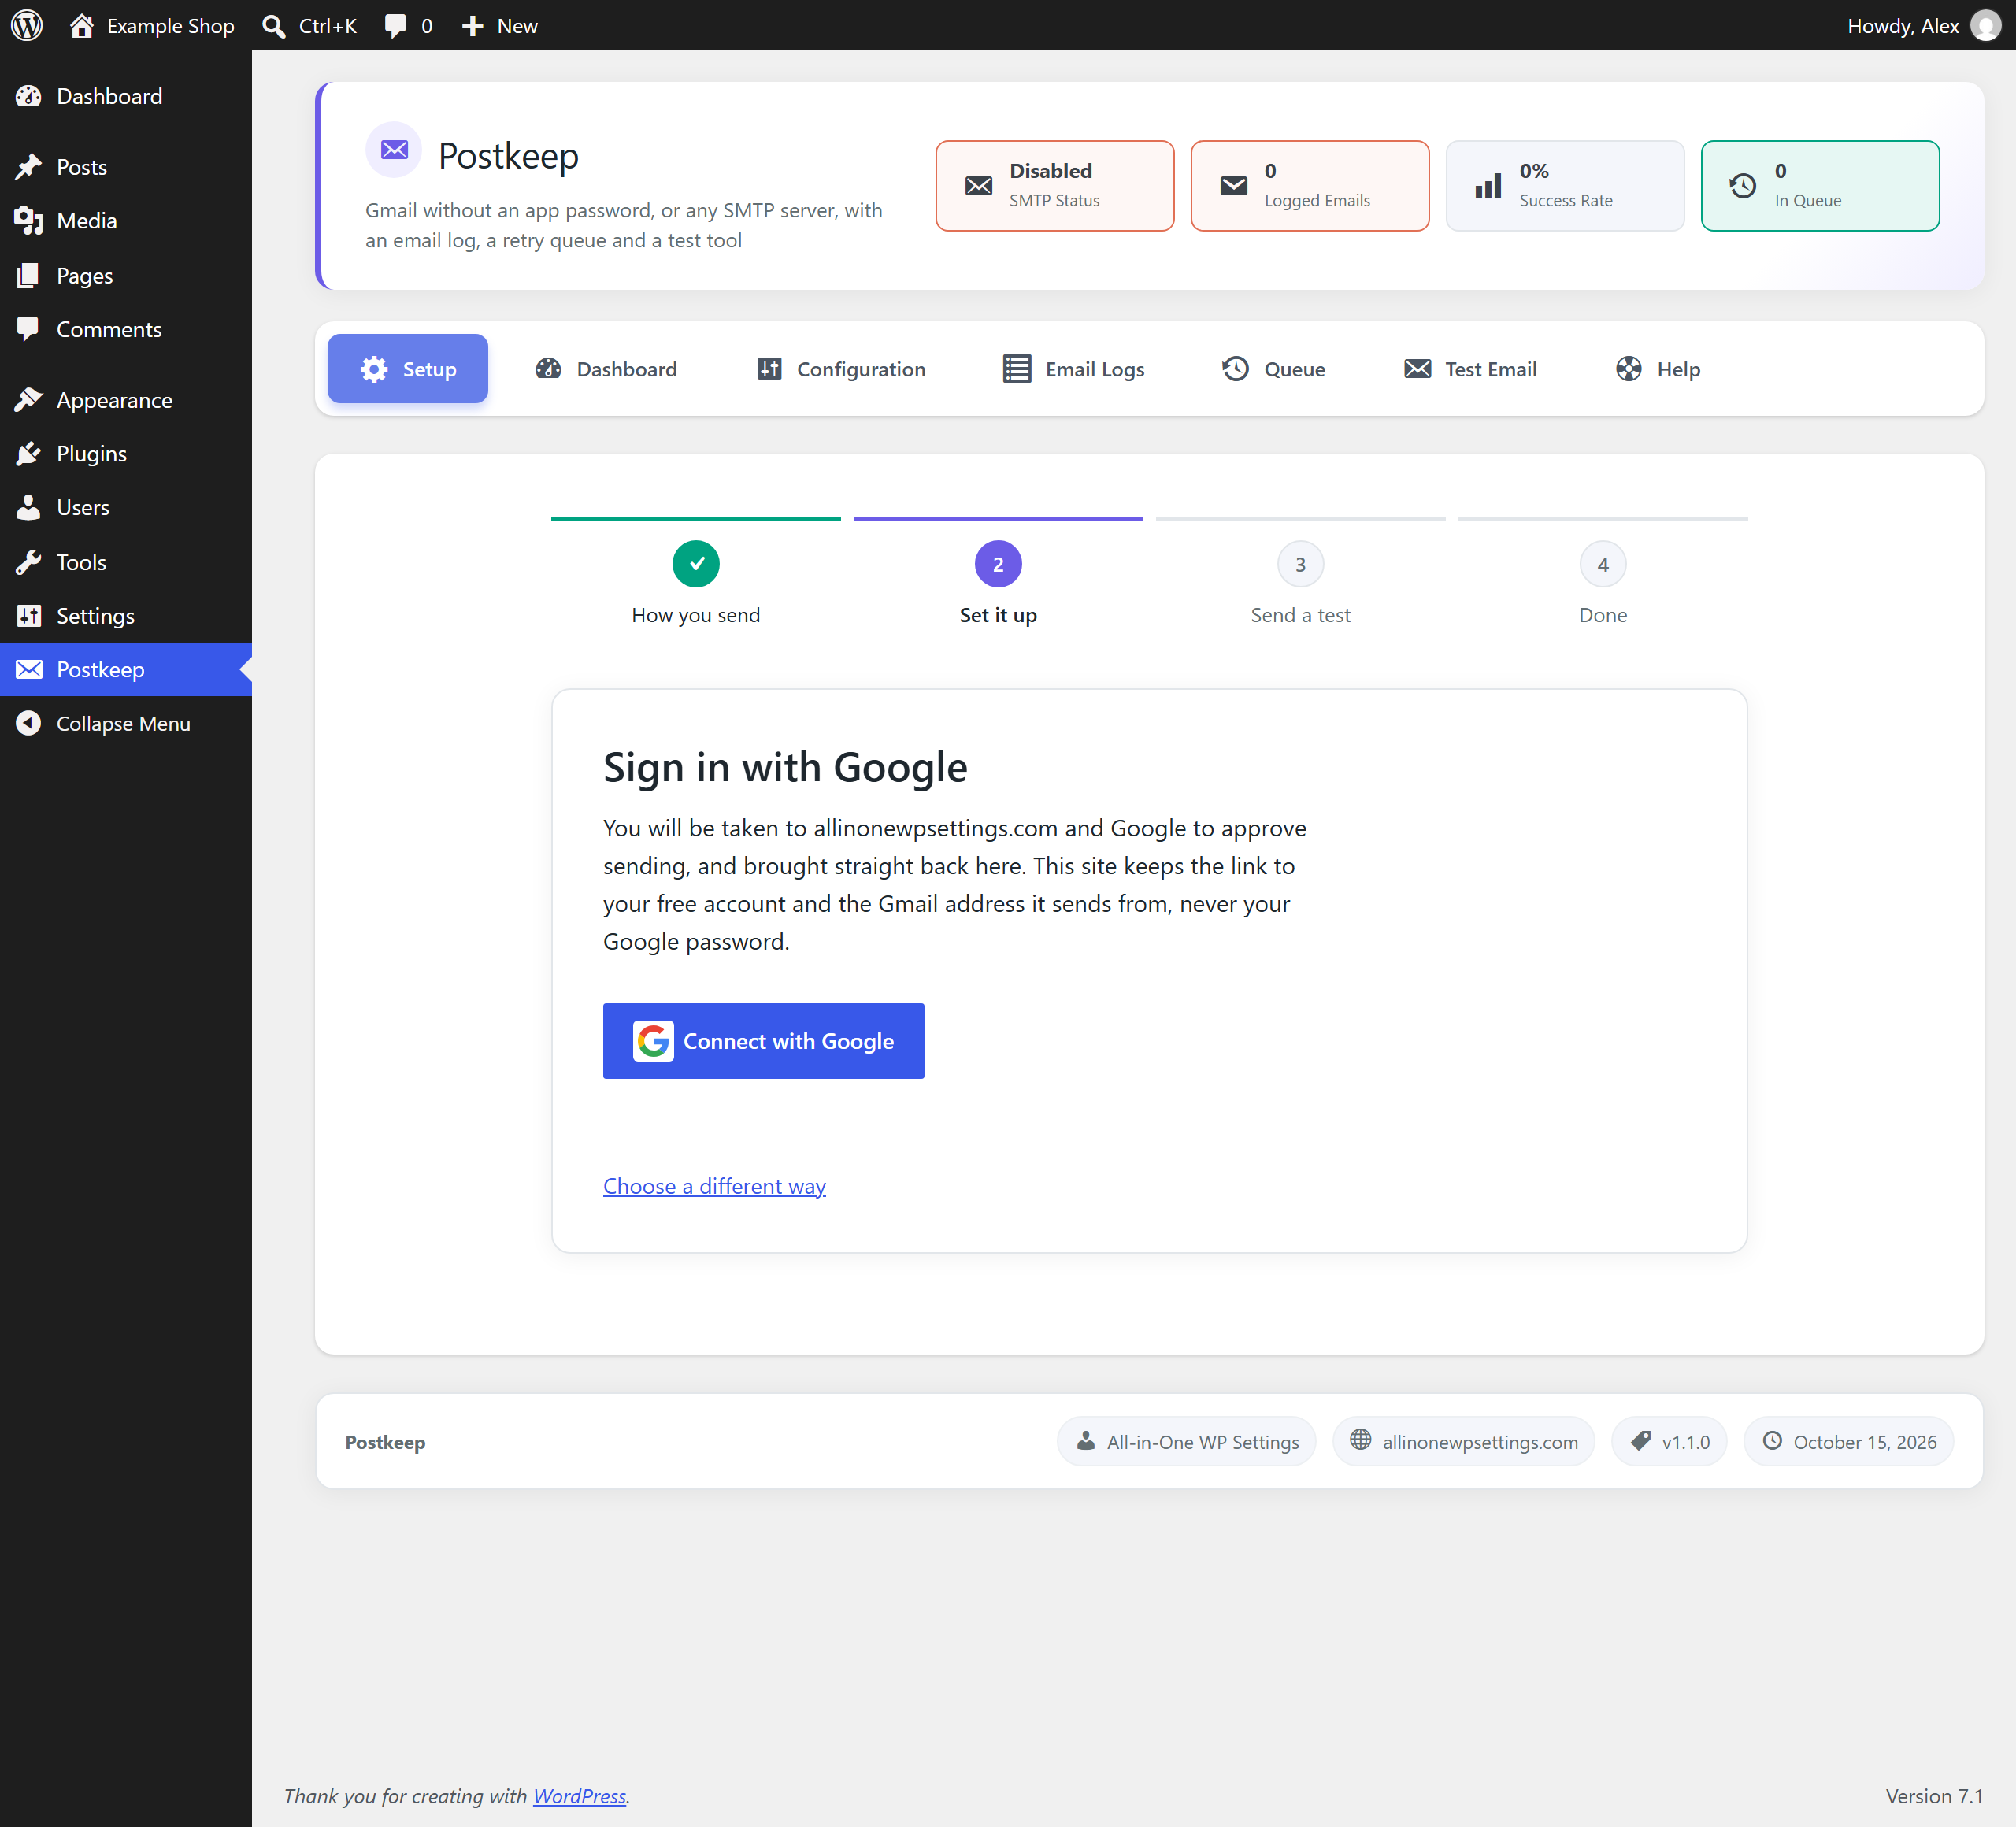
- For Gmail, click “Connect with Google” and sign in; the account starts sending as soon as Google sends you back. For any other provider, enter the host and login details, turn “SMTP Status” on and save.
- Send yourself a message from the Test Email tab.
FAQ
-
Do I need an account for Postkeep to work?
-
Only for the free Gmail connection. Every other provider, and Gmail with an app password, works with no account and contacts no service.
-
What does the free account allow?
-
One site connected to Gmail through the service. Connecting a second site from the same account moves the connection to it; the service’s page says so before it does.
-
Which Google permission does the plugin ask for?
-
Send-only (
https://www.googleapis.com/auth/gmail.send). The plugin cannot read, search or delete your mail. -
Microsoft requires OAuth2, and the free plugin has no shared Microsoft app to sign in with. Choose OAuth2 on the Outlook card and enter the Client ID and Client Secret of an app registered in your own Azure portal; the plugin walks you through it. Microsoft sign-in without an Azure app is part of All-in-One WP Settings.
-
The connection says it is paused. What now?
-
Then the free Gmail connection is closed for the moment. It is a service, and it can be paused for a while — when it is, the plugin says so instead of failing quietly, and an account you have already connected is kept: sending through it resumes when the connection reopens. Meanwhile Gmail works with an app password: choose Gmail, enter the address and the app password, and save.
-
Where are my passwords stored?
-
In your site’s database, encrypted with your site’s security keys (AES-256-GCM). A backup or export of the database does not contain them in the clear. If the security keys are ever changed, the plugin tells you which credential to enter again.
One exception, and the plugin says so on its own page when it applies: the encryption needs PHP’s openssl extension, which nearly every host has. Without it a password is only encoded, not encrypted, and the Configuration tab shows a warning asking you to have openssl enabled.
-
Can I set the SMTP password in wp-config.php instead?
-
Yes:
define( 'POSTKEEP_SMTP_PASSWORD', 'your password' );takes precedence over the saved one, and the settings page says so. -
Where do I get help?
-
In the plugin’s support forum on WordPress.org. The Help tab has a summary of your setup to paste into your post. Passwords, tokens and the licence key are never in it, and every e-mail address in it is masked.
Reviews
There are no reviews for this plugin.
Contributors & Developers
“Postkeep – One Click SMTP Setup and Email Log” is open source software. The following people have contributed to this plugin.
Contributors
“Postkeep – One Click SMTP Setup and Email Log” has been translated into 1 locale. Thank you to the translators for their contributions.
Translate “Postkeep – One Click SMTP Setup and Email Log” into your language.
Interested in development?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Changelog
1.2.0 — 2026-10-18
- Your free licence key is now stored encrypted with your site’s security keys, like the activation token beside it. A key saved by an earlier version is encrypted the first time anyone opens the WordPress admin after the update. Going back to 1.1.1 or older afterwards is not recommended: that version cannot read the encrypted key, so Gmail sending stops until its daily check unlinks the site and you click “Connect with Google” again.
- When Google stops accepting the Gmail connection, Postkeep now finds out and says so. Before, the Configuration tab could keep saying “Gmail connected” while every email failed. Now a refused email is sent again once with a fresh token, and when the connection is really gone the card reads “Reconnect required”.
- The retry queue is on by default, as the Configuration tab always showed it. On a site set up with Connect with Google or the setup wizard, a failed email was logged but not retried until someone saved the Configuration tab. A queue you switched off stays off.
- The retry queue waits as long as it says, whatever your site’s time zone: 5 minutes, then 15 minutes, on your site’s clock. Before, the wait was measured in UTC, so on a site west of UTC it grew by hours and east of UTC it disappeared.
- A failed test or send now shows what the mail server said, also with Debug Logging off, on the Test Email tab and in the email log. A reply of several lines no longer shows its last sentence twice.
- The Help tab’s summary is safe to paste in a public forum: every email address in it is masked, also one a server named in a failure line, and no part of the licence key is shown. It now says “debug logging” for the Debug Logging switch.
- Your licence key is no longer part of a web address when the plugin checks the Gmail connection. It is sent inside the request, where web server and proxy logs do not keep it.
- Saving the Configuration tab no longer moves sending off a connected Gmail account. If you clicked another provider card to look at it and then saved, mail used to switch to the manual SMTP settings. “Use manual SMTP for sending” is now the one way off the connected account.
- The Configuration form saves without asking you to retype a password it already has, and choosing “None” under Encryption no longer stops it from saving.
- For an email sent through the Gmail API, the email log names the Gmail API instead of the SMTP server stored in your settings.
- A new provider card for Microsoft 365 / Exchange Online fills in smtp.office365.com, port 587, STARTTLS; the Outlook card is now for personal Outlook.com accounts. When Microsoft 365 refuses a password because SMTP AUTH is switched off, the hint says which switch. A sign-in a server refuses with code 550 is reported as a sign-in problem, not a refused recipient.
- The Test Email tab shows Debug Logging as information, not with a green tick: it writes the SMTP conversation to the server’s error log and belongs off on a live site.
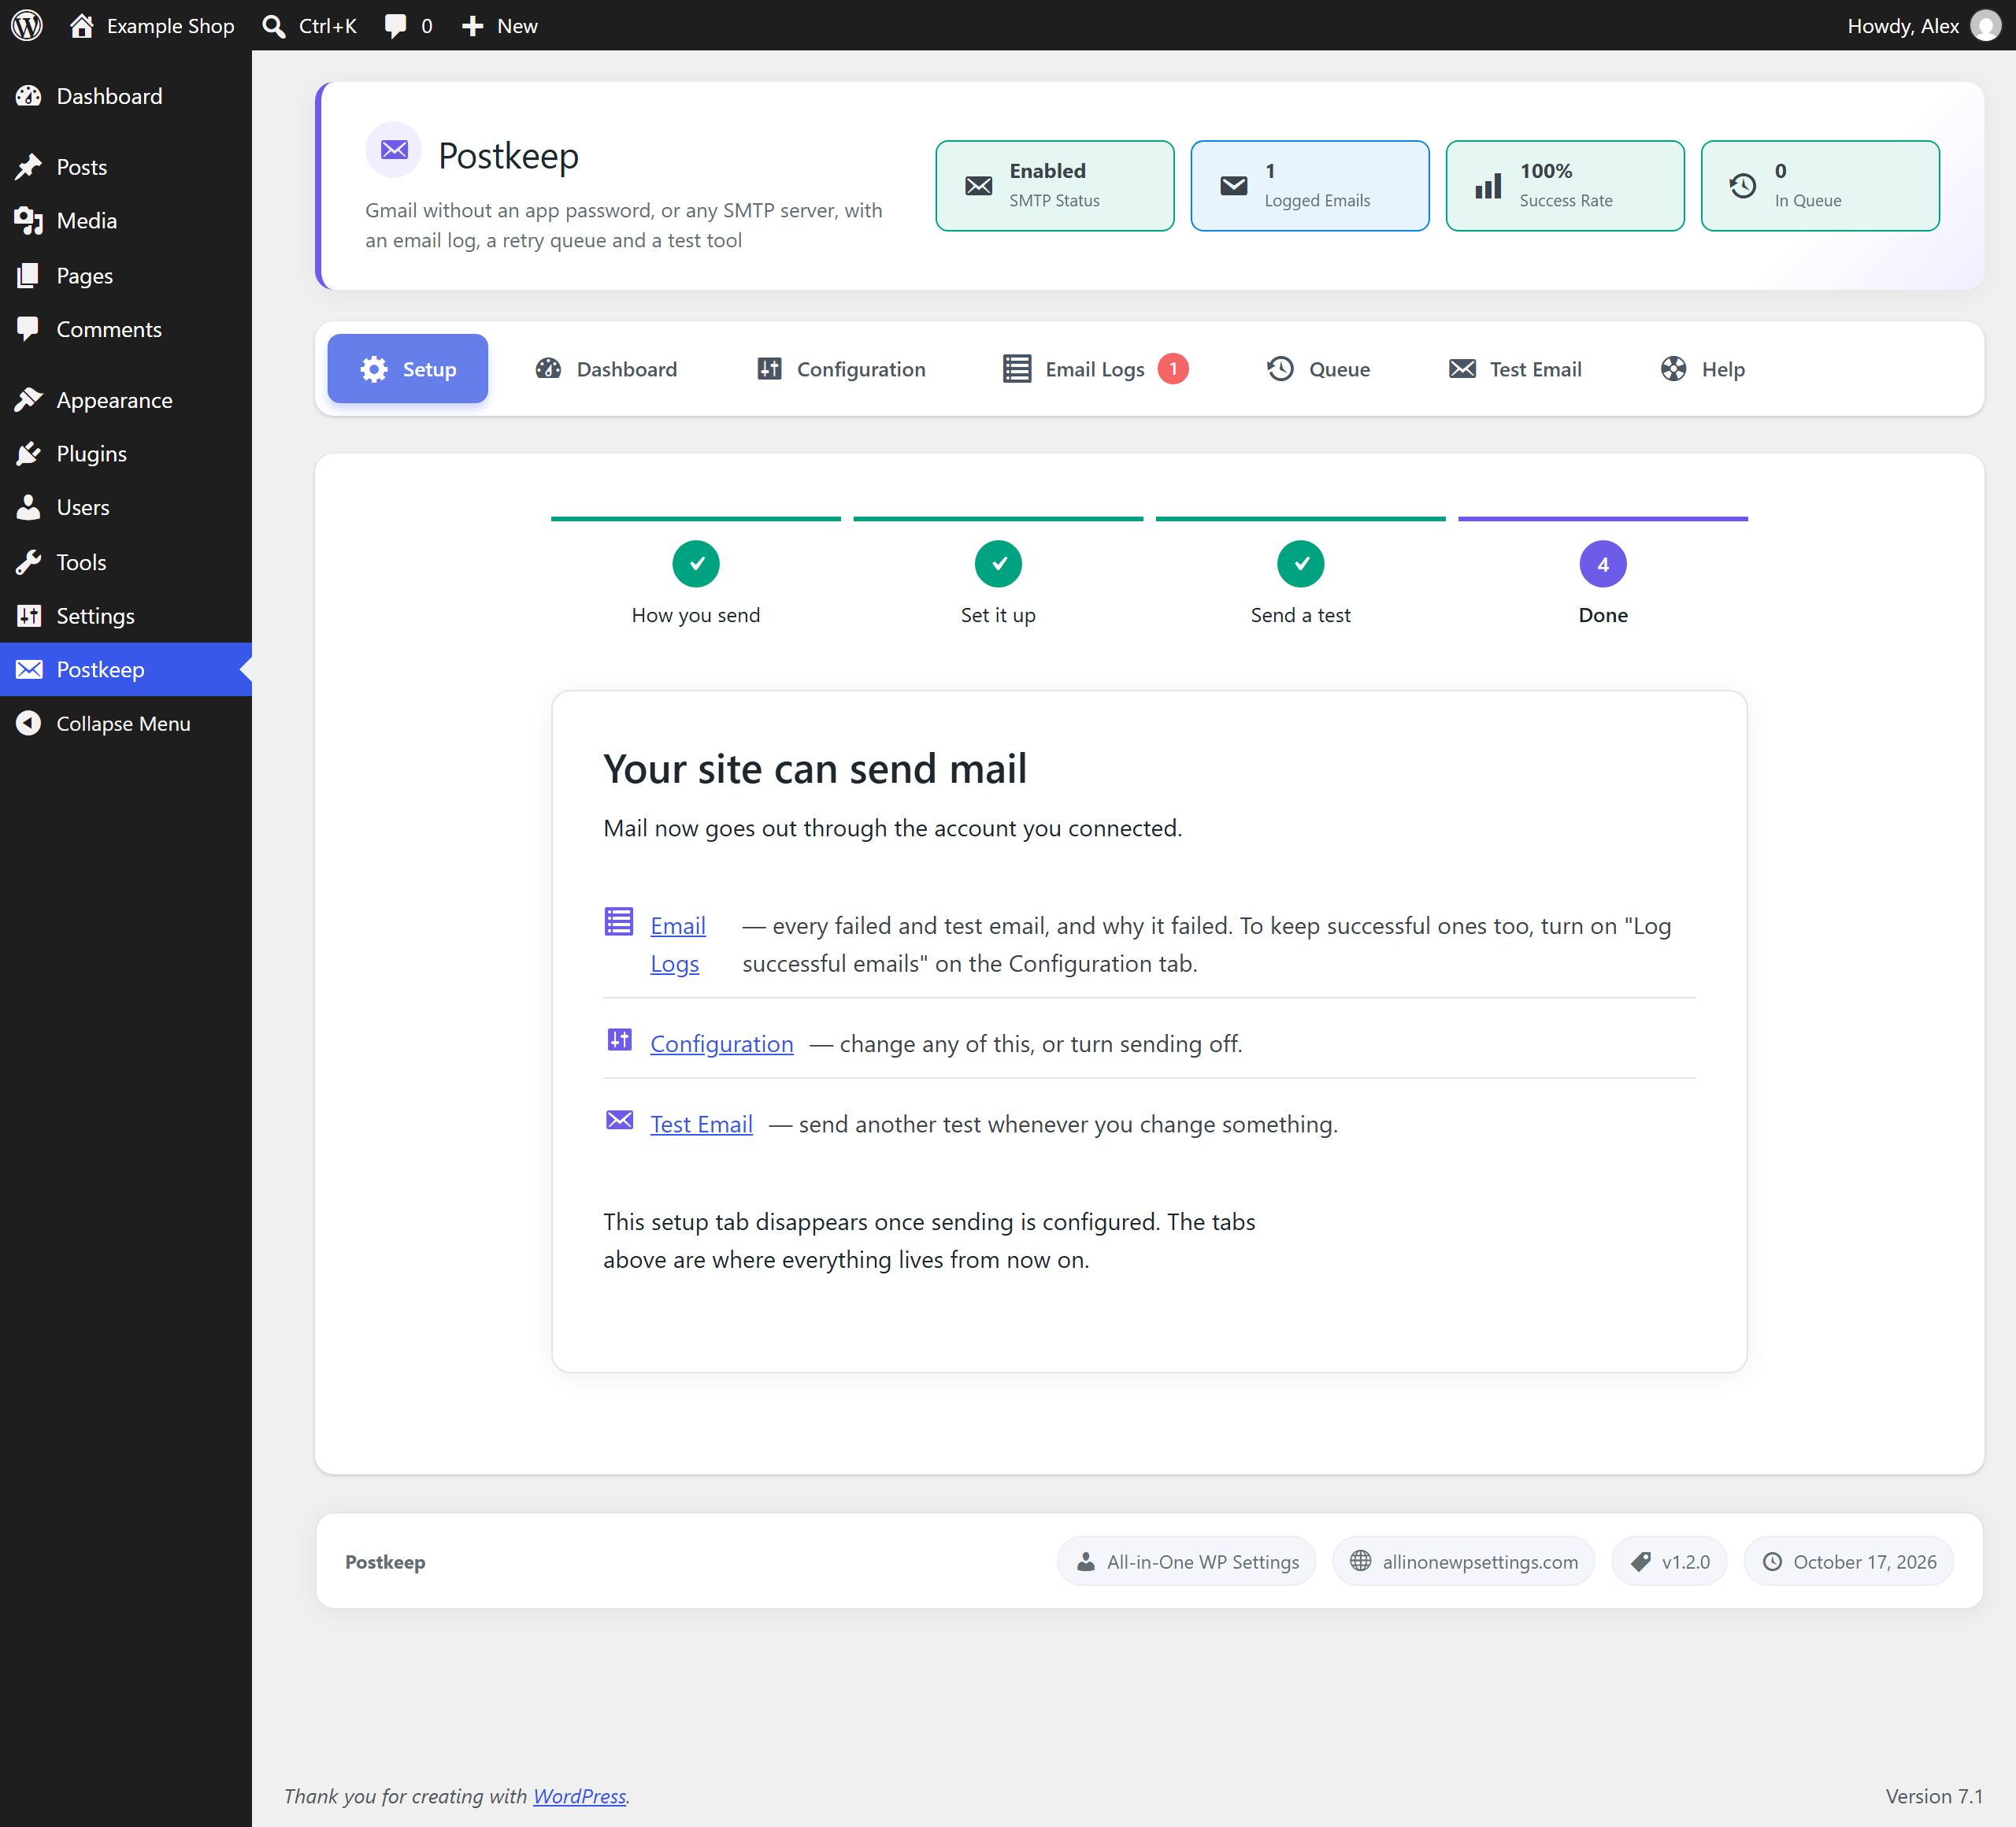
- The setup wizard’s last step no longer says the email log keeps every mail. By default it keeps failed and test emails, and the step says where to keep successful ones too.
- The Queue tab shows no Next Retry time on finished emails, and its action icons stay in their columns.
- On the Configuration tab, the help text under Server, Encryption and Port no longer touches the Username and Password labels below it.
- The Shared Hosting card shows its server pattern as mail.yourdomain.com.
1.1.1
- Every email in a request now goes through your configured SMTP server; before, only the first did, and later ones such as a WooCommerce customer email could bypass it.
1.1.0
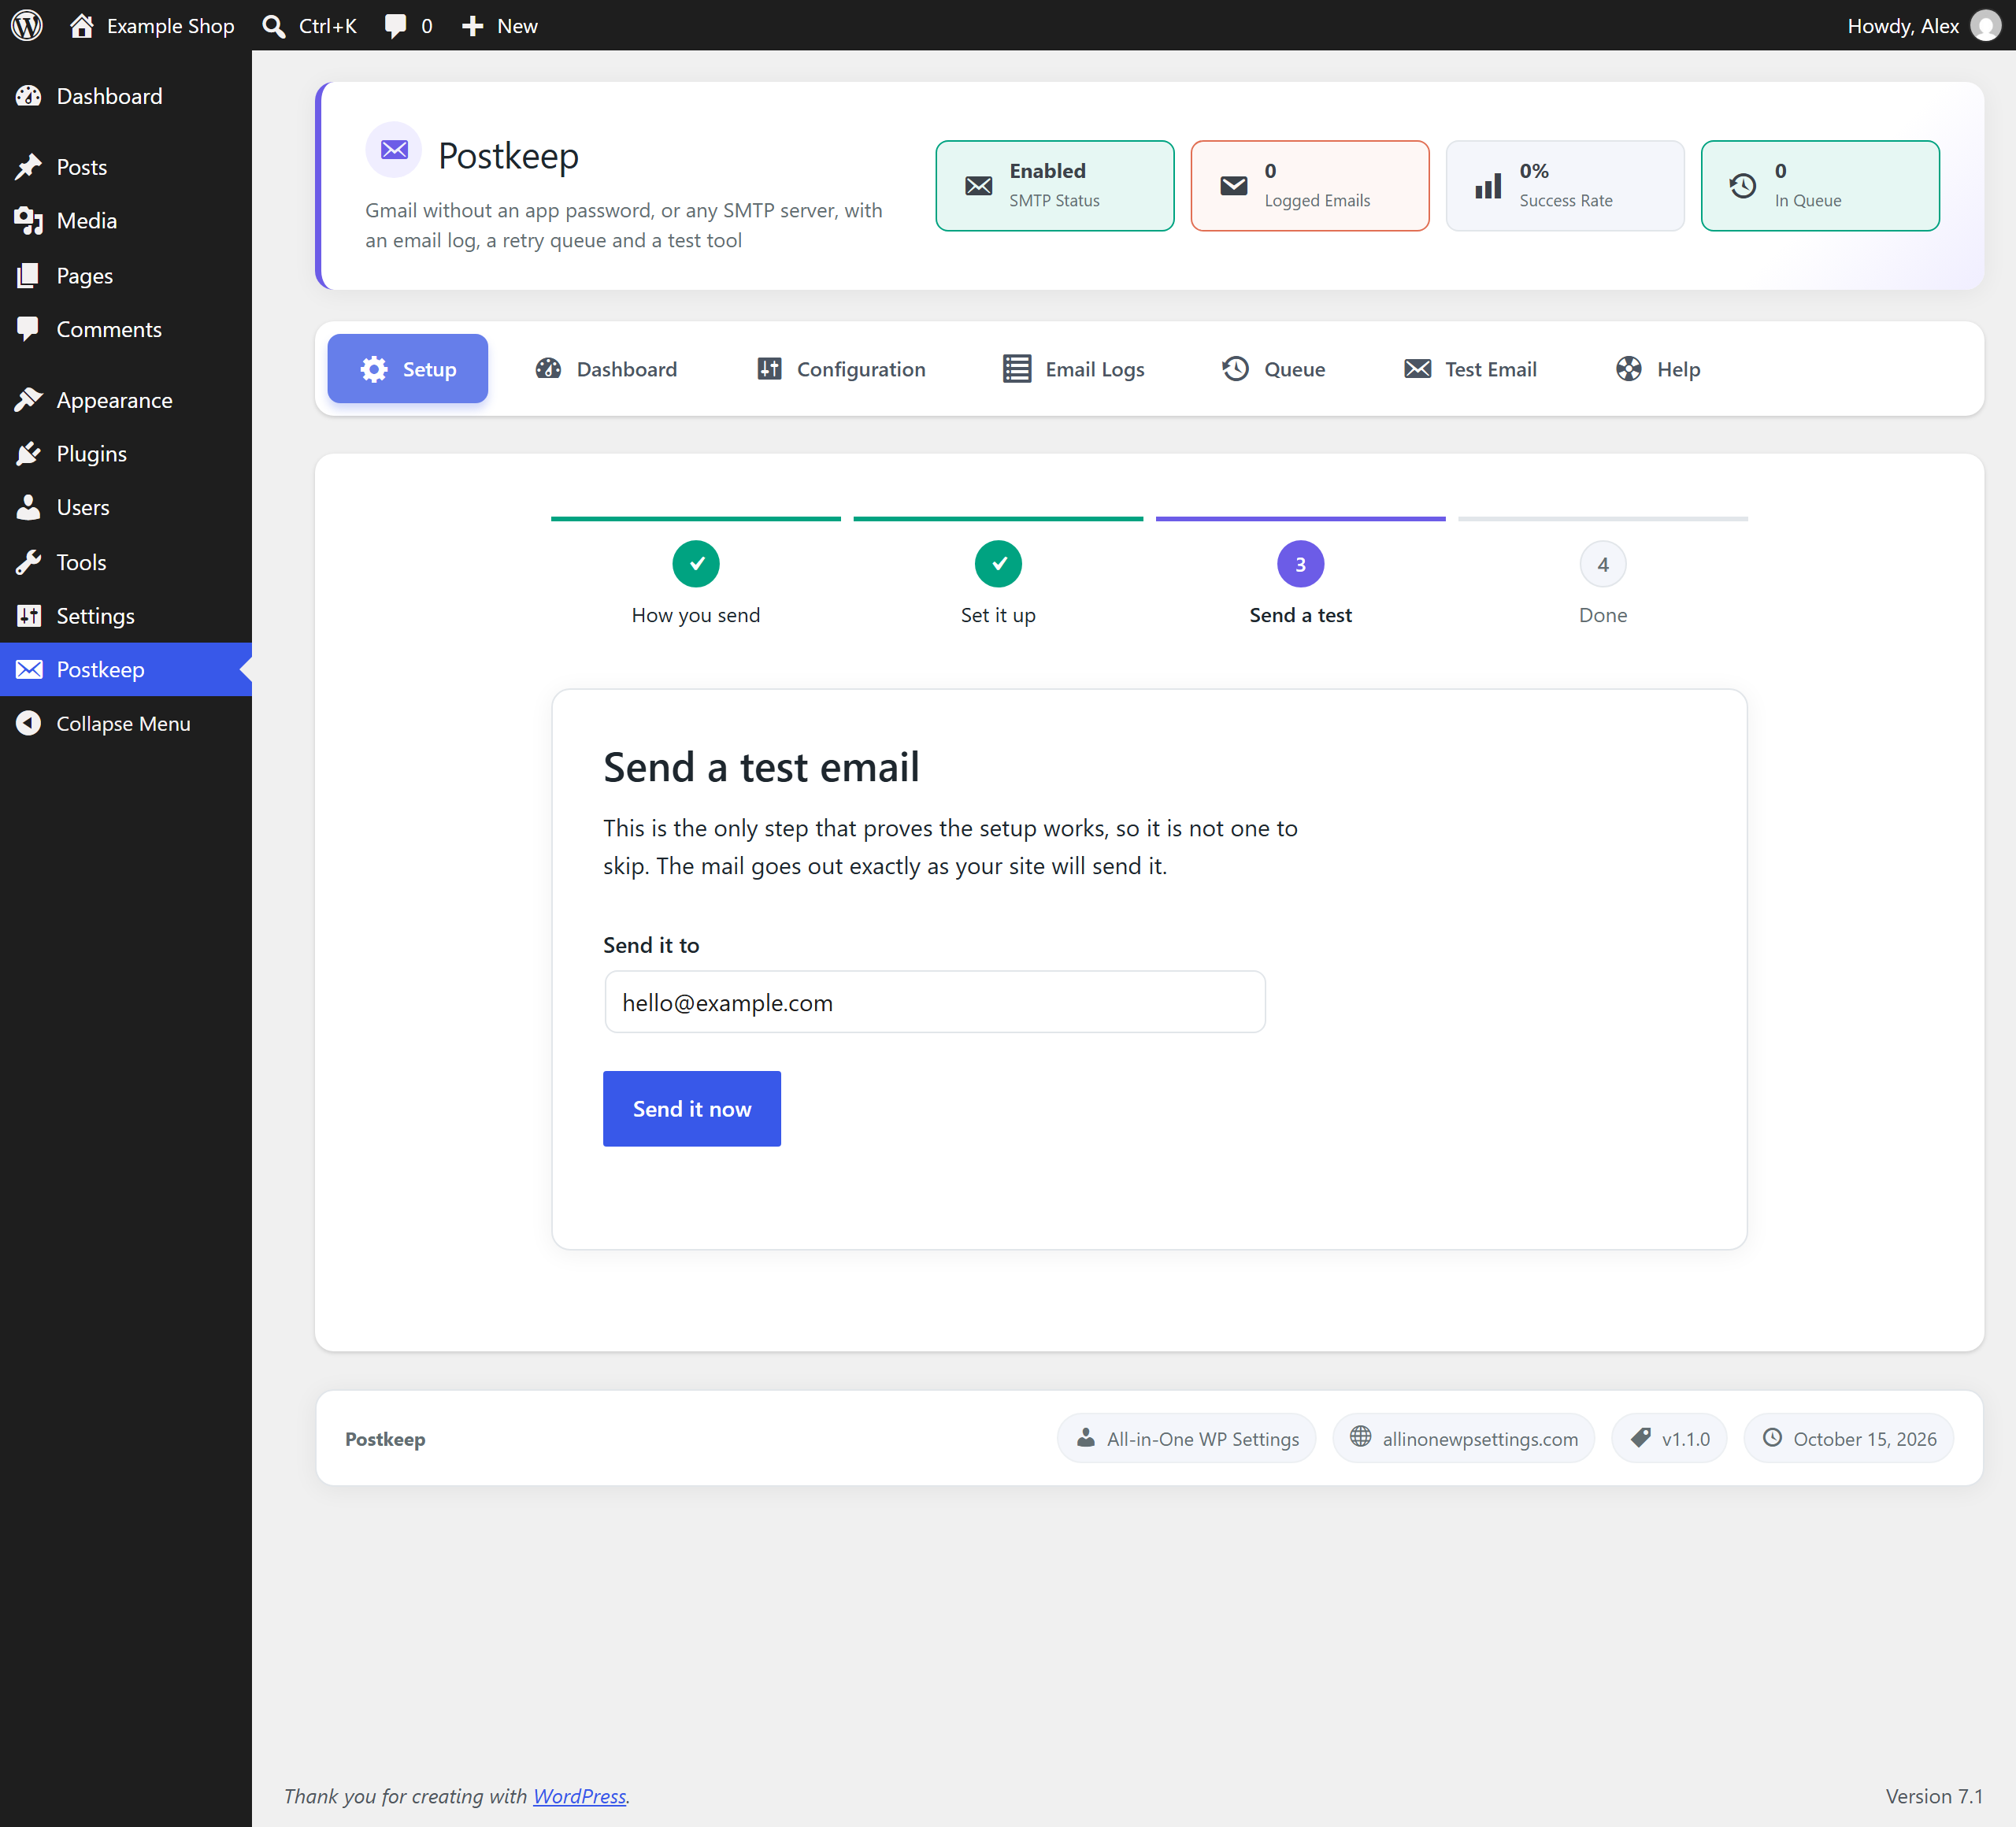
- New: a setup wizard. It asks one question per screen — how the site should send mail, the details for that choice, a test email — and ends by showing what is sending and where the log is.
- A new install opens on the wizard, and activating the plugin takes you there once. Bulk and network activations, and sites that already send mail, are not redirected.
- The wizard is a starting point, not a requirement: every other tab stays one click away, “I will configure it myself” goes straight to the Configuration tab, and the wizard disappears once sending is configured.
- After you approve Gmail at Google, you come back to the screen you started from — the wizard’s test step, or the Configuration tab — instead of always the Configuration tab.
- After connecting Gmail from the Configuration or Test Email tab, the confirmation offers “Send a test email” instead of sending you to the Configuration tab.
- Saving settings now changes only the settings that were on the screen you saved; everything else keeps its saved value instead of falling back to a default.
- An empty or invalid port no longer saves as port 0; the port you had is kept.
- The email log now records the address a request really came from. It used to trust a header that any visitor can set, so a log entry could show an address the visitor made up.
- Deleting the plugin now also removes one small setting it used to leave in the database.
- The Configuration tab no longer shows a Microsoft card that could not connect. Outlook and Microsoft 365 still send through the Outlook provider card, with OAuth2 and your own Azure app.
- When a sign-in fails, the email log’s advice no longer suggests a one-click connection for Outlook, which this plugin does not offer; it points to OAuth2 with your own Azure app instead.
- The Dashboard no longer shows a red bar at the top of the page that says only “Needs attention” when mail has failed; the note stays on the Failed card. The Test Email tab’s “SMTP Status” line, shown when sending is off, stays in its list too.
- On the Configuration tab, Encryption now comes before Port, and choosing SSL or TLS sets the usual port (465 or 587) unless you typed a port of your own.
- Sending a test email through Gmail no longer writes PHP warnings to the debug log.
- Connecting Gmail from the Configuration tab now makes it the sending method straight away, also after a Disconnect or when the site sent through its own server before. The “Use this account for sending” button remains for a site that saves a different provider after connecting.
- Disconnecting Gmail no longer leaves Postkeep switched on with nothing to send through: without a complete SMTP setup it switches off, so WordPress sends mail its own default way, and the page says how mail goes out now.
- On the Configuration tab, the Encryption and Log Retention lists are the same height as the fields beside them.
1.0.2
- Connecting Gmail now finishes the job. Sign in once and the account starts sending; before this, signing in left it connected but not sending, and you had to pick Gmail in the provider list and save — which the plugin’s own description did not say. A site that is already sending through its own SMTP server is never switched over silently: the connected card offers a “Use this account for sending” button, and the choice stays yours.
- Saving the Configuration form no longer asks for an SMTP host when there is none to give — a Gmail connection has no SMTP server — and turning SMTP Status off no longer asks for the settings of the thing being turned off.
- Debug output in the admin JavaScript could print a submitted SMTP password — and a bring-your-own OAuth client secret — in cleartext to the browser console when saving the Configuration tab failed. It is removed. The output was never transmitted anywhere: it went to your own browser’s console and no further, only the signed-in administrator who pressed Save saw it, it needed a failed save (a successful one printed nothing), and nothing was written to a file, a database row or a log. If you believe a failed save was captured on a screen share or a recording, rotate the app password, and the client secret too if you use your own OAuth client.
- The Test Email tab’s status panel said “From Email Set: Not set” when Gmail was connected. It now names the address mail actually goes out from — the connected account’s own. Only the panel was wrong: mail sent through a connected account has always gone out from that account.
- Signing in to Gmail no longer asks you to press Connect twice. After the e-mail confirmation the plugin now goes on to Google by itself; before, it came back to the settings page and the sign-in had to be started again. If it still cannot start, you stay on the page with a sentence that says why and the button is there.
- The connected card no longer says “This account is connected but is not sending” for a moment on the way back from Google and then take it back. While it reads the connection’s real state it says “Finishing the sign-in…” and nothing else.
- When the Gmail sign-in cannot start, the plugin says so instead of saying the connection service could not be reached. It told you to check a connection that was working.
- The description and the installation steps now say what the plugin actually does, step by step.
1.0.1
- Fixed a fatal error on activation on WordPress 6.8 and older. Those versions ship PHPMailer without its OAuthTokenProvider interface, and the plugin required that file outright. It is now loaded only when WordPress has it, and declared by the plugin when WordPress does not. Nothing else changed.
1.0.0
- First release: the SMTP module of All-in-One WP Settings on its own, with the free Gmail connection.